目标达成 感谢每一位支持者 — 我们达成了 100% 目标!

目标: 1000 元 · 已筹: 1359 元

100%

CVE-2022-30190 PoC — Microsoft Windows Support Diagnostic Tool 操作系统命令注入漏洞

来源
关联漏洞
标题: Microsoft Windows Support Diagnostic Tool 操作系统命令注入漏洞 (CVE-2022-30190)
Description:Microsoft Windows Support Diagnostic Tool是美国微软(Microsoft)公司的收集信息以发送给 Microsoft 支持的工具。 Microsoft Windows Support Diagnostic Tool (MSDT)存在操作系统命令注入漏洞。以下产品和版本受到影响:Windows 10 Version 1809 for 32-bit Systems,Windows 10 Version 1809 for x64-based Systems,Windows
Description
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
介绍
# FollinaScanner
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
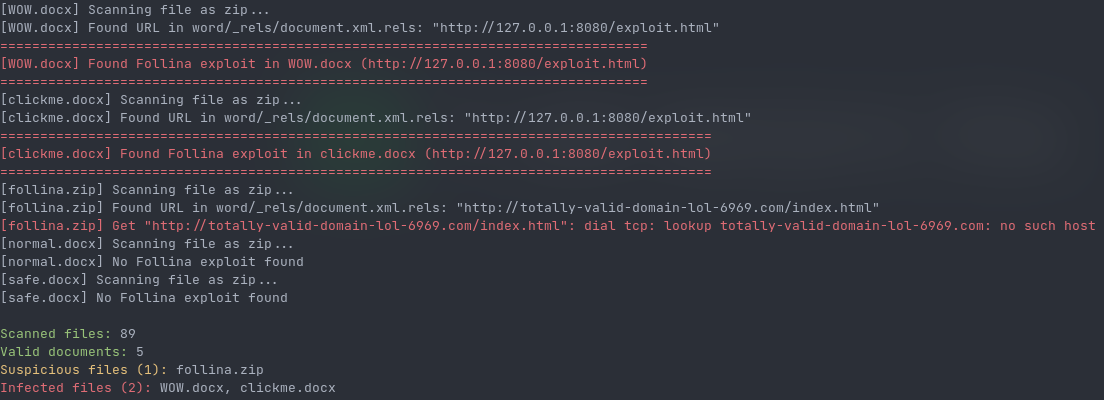
![Screenshot](https://raw.githubusercontent.com/ErrorNoInternet/FollinaScanner/main/screenshots/screenshot0.png)
*(Note: "Suspicious files" means files that have a URL in them but isn't working)*

## Compiling
```sh
git clone https://github.com/ErrorNoInternet/FollinaScanner
cd FollinaScanner
go build
```

## Usage
```sh
# Scan the current directory
./follina-scanner -r .

# Scan a specific file
./follina-scanner amogus.docx
```
Use `./follina-scanner --help` for a list of arguments

<sub>If you would like to modify or use this repository (including its code) in your own project, please be sure to credit!</sub>
文件快照

登录后查看神龙缓存的 POC 文件快照

登录查看
备注
    1. 建议优先通过来源进行访问。
    2. 本地 POC 快照面向订阅用户开放;当原始来源失效或无法访问时,本地镜像作为订阅权益的一部分提供。
    3. 持续抓取、验证、维护这份 POC 档案需要不少投入,因此本地快照已纳入付费订阅。您的订阅是让这份资料能继续走下去的关键,由衷感谢。 查看订阅方案 →