目标达成 感谢每一位支持者 — 我们达成了 100% 目标!

目标: 1000 元 · 已筹: 1359 元

100%

CVE-2017-8464 PoC — 多款Microsoft产品访问控制错误漏洞

来源
关联漏洞
标题: 多款Microsoft产品访问控制错误漏洞 (CVE-2017-8464)
Description:Microsoft Windows等都是美国微软(Microsoft)公司的产品。Microsoft Windows是一套个人设备使用的操作系统。Microsoft Windows XP是一套PC和平板电脑使用的操作系统。Windows是一种桌面操作系统。 Microsoft Windows中的Windows Shell中存在访问控制错误漏洞。攻击者可借助特制的.LNK文件利用该漏洞执行任意代码。以下版本受到影响:Microsoft Windows Server 2008 SP2和R2 SP1,Windo
介绍
# CVE-2017-8464-EXP
Support x86 and x64

Just for test

Lnk file from:
https://github.com/rapid7/metasploit-framework/pull/8767

Thanks to ykoster

Small change,replace the dll file,fix the bug of crashing explorer.exe.(ykoster has fixed this bug)

POC:

x86:
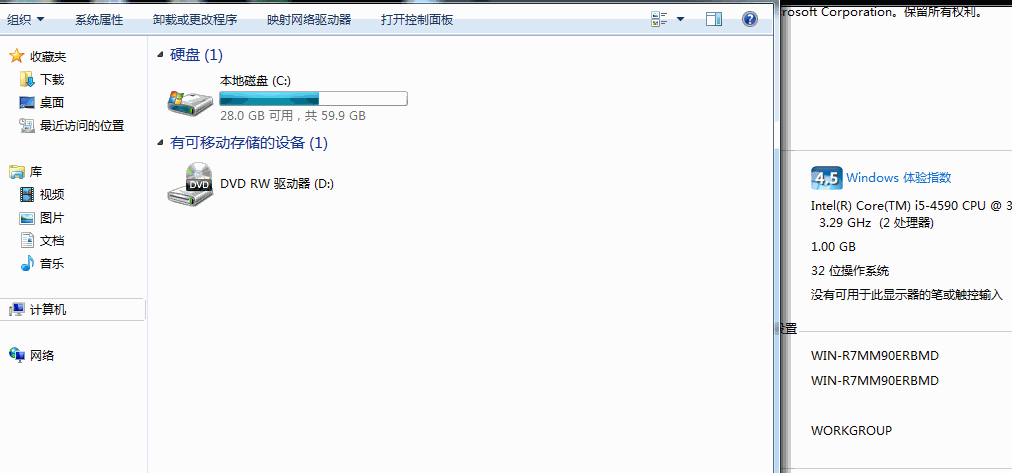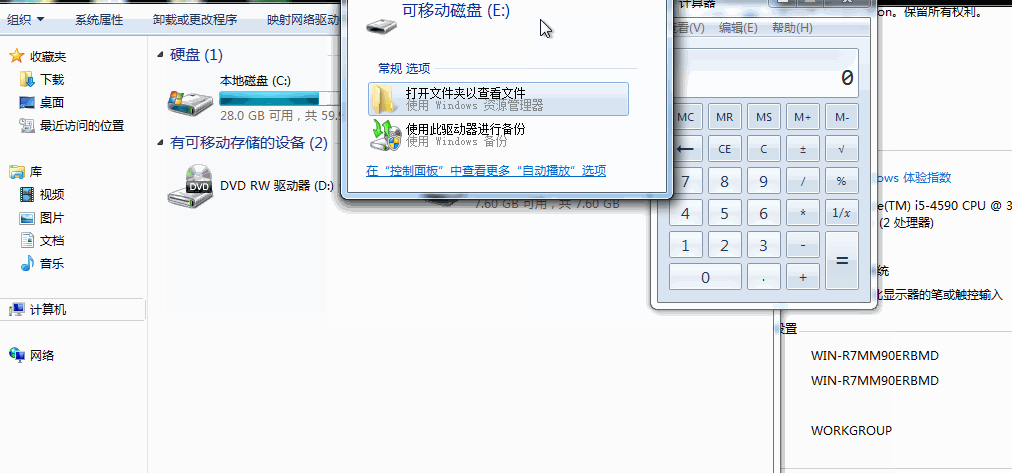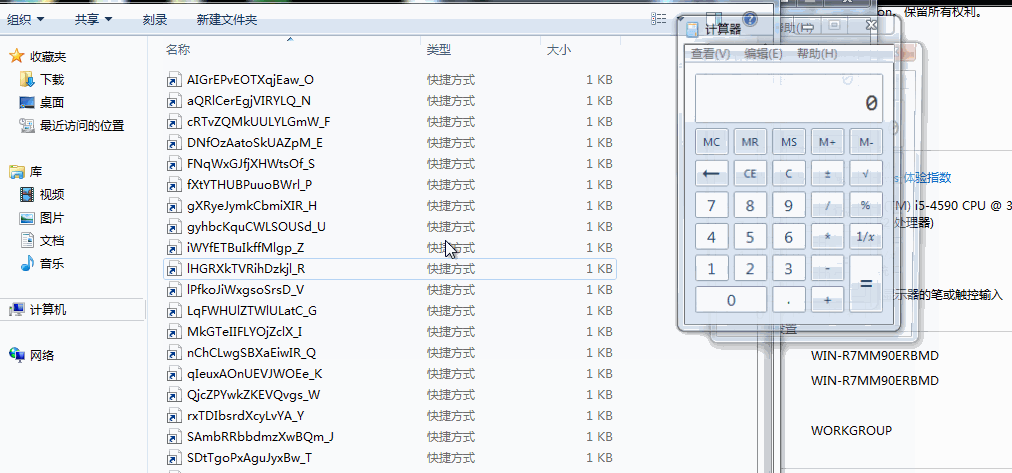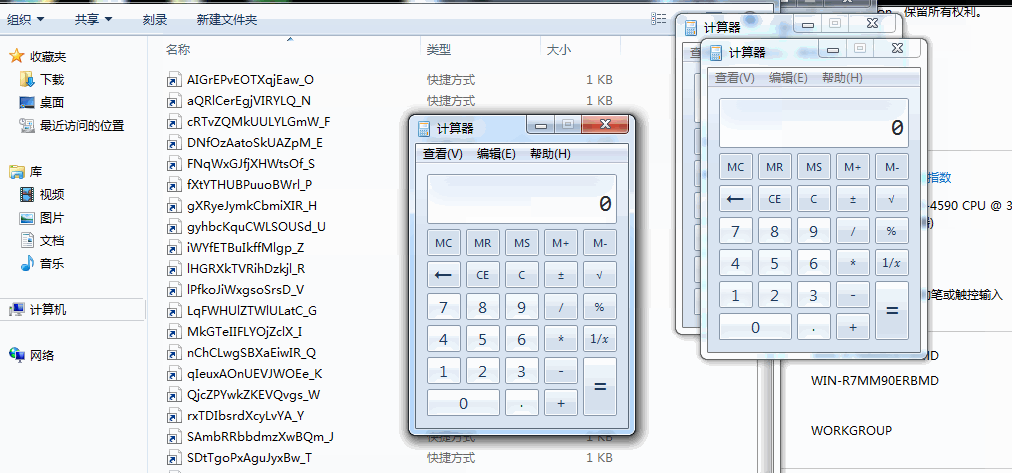
![Alt text](https://raw.githubusercontent.com/3gstudent/CVE-2017-8464-EXP/master/x86.gif)

x64:

![Alt text](https://raw.githubusercontent.com/3gstudent/CVE-2017-8464-EXP/master/x64.gif)

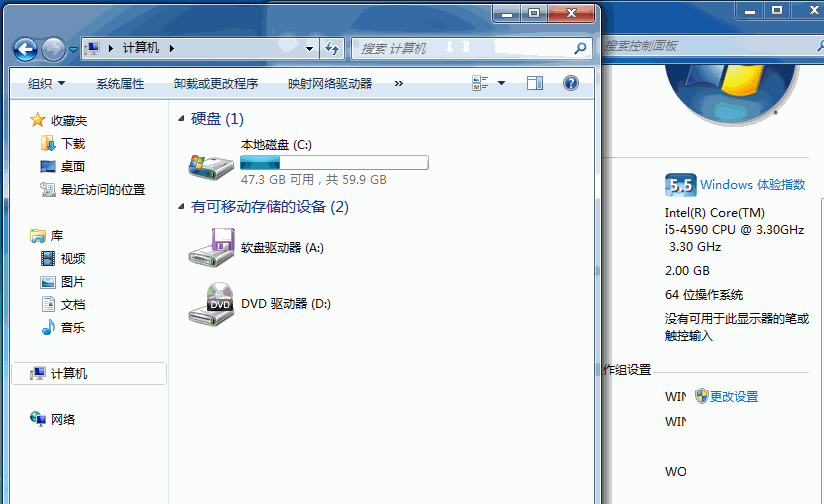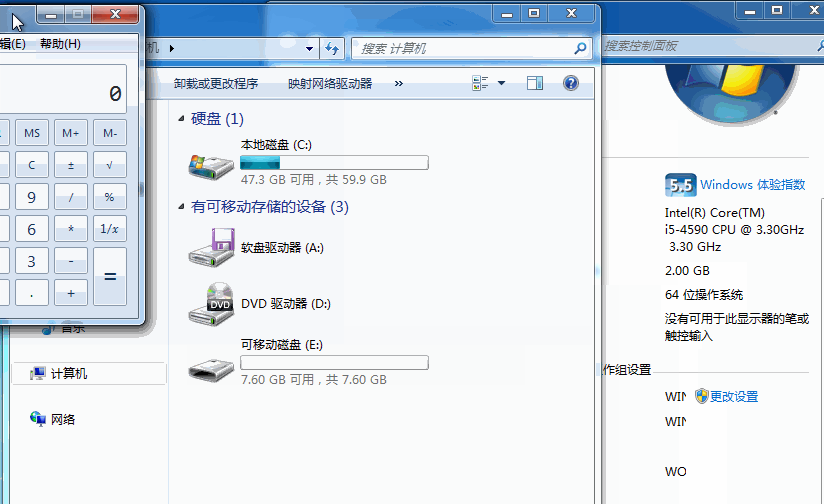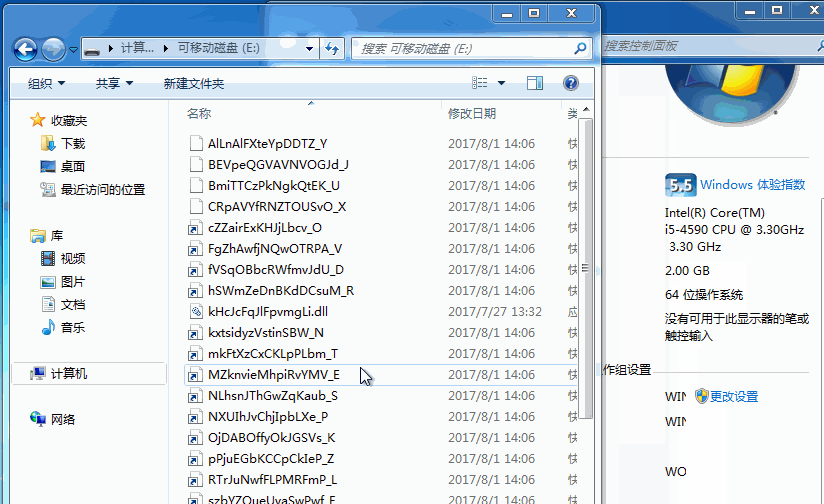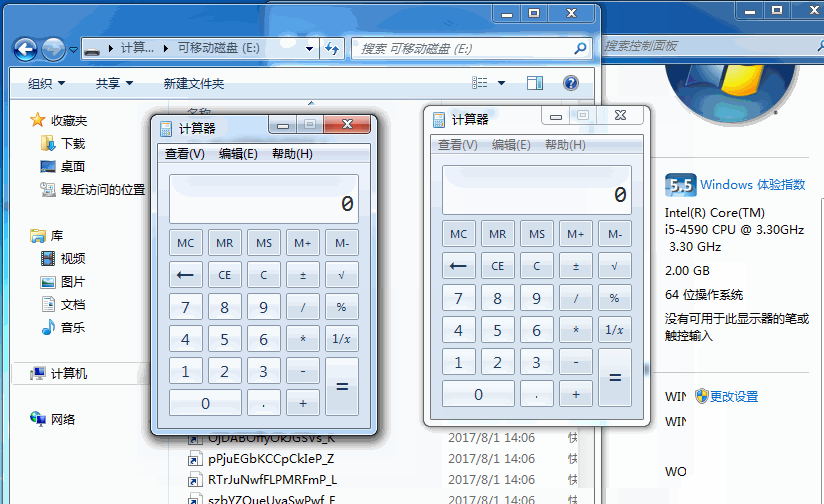
If you can determine the USB drive,one LNK file is enough,like this:
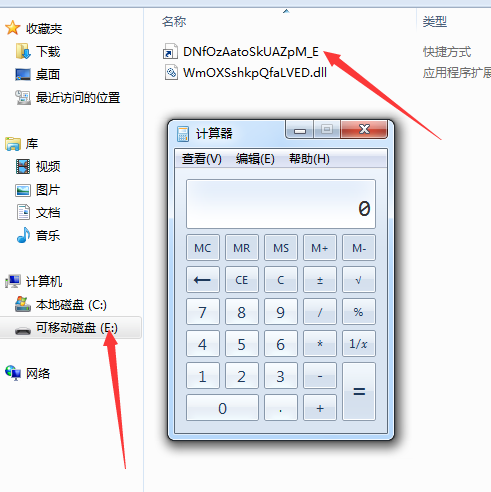
![Alt text](https://raw.githubusercontent.com/3gstudent/CVE-2017-8464-EXP/master/poc1.png)

More details:

https://3gstudent.github.io/3gstudent.github.io/Windows-Lnk%E8%BF%9C%E7%A8%8B%E4%BB%A3%E7%A0%81%E6%89%A7%E8%A1%8C%E6%BC%8F%E6%B4%9E(CVE-2017-8464)%E5%88%A9%E7%94%A8%E6%B5%8B%E8%AF%95/
文件快照

登录后查看神龙缓存的 POC 文件快照

登录查看
备注
    1. 建议优先通过来源进行访问。
    2. 本地 POC 快照面向订阅用户开放;当原始来源失效或无法访问时,本地镜像作为订阅权益的一部分提供。
    3. 持续抓取、验证、维护这份 POC 档案需要不少投入,因此本地快照已纳入付费订阅。您的订阅是让这份资料能继续走下去的关键,由衷感谢。 查看订阅方案 →