CVE-2024-26152— Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Quick assessment
Affected
HumanSignal label-studio
Exploitation
No confirmed in-the-wild exploitation; assess based on exposure
Recommended action
Check the vendor advisory and references for a fixed version. If immediate upgrade is impossible, restrict exposure and increase monitoring.
Label Studio是Heartex开源的一个开源数据标注工具。允许您使用简单明了的 UI 标记音频、文本、图像、视频和时间序列等数据类型,并导出为各种模型格式。 Label Studio 1.11.0之前版本存在安全漏洞,该漏洞源于存在跨站脚本(XSS)漏洞。
Possible ATT&CK Techniques 2 AI
T1059 · Command and Scripting Interpreter T1189 · Drive-by Compromise
Get alerts for future matching vulnerabilities
Log in to subscribe
I. Basic Information for CVE-2024-26152
Vulnerability Information
Have questions about the vulnerability? See if Shenlong's analysis helps!
View Shenlong Deep Dive ↗
Although we use advanced large model technology, its output may still contain inaccurate or outdated information.Shenlong tries to ensure data accuracy, but please verify and judge based on the actual situation.
Vulnerability Title
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Source: CVE Program / CVE List V5
Vulnerability Description
### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project.
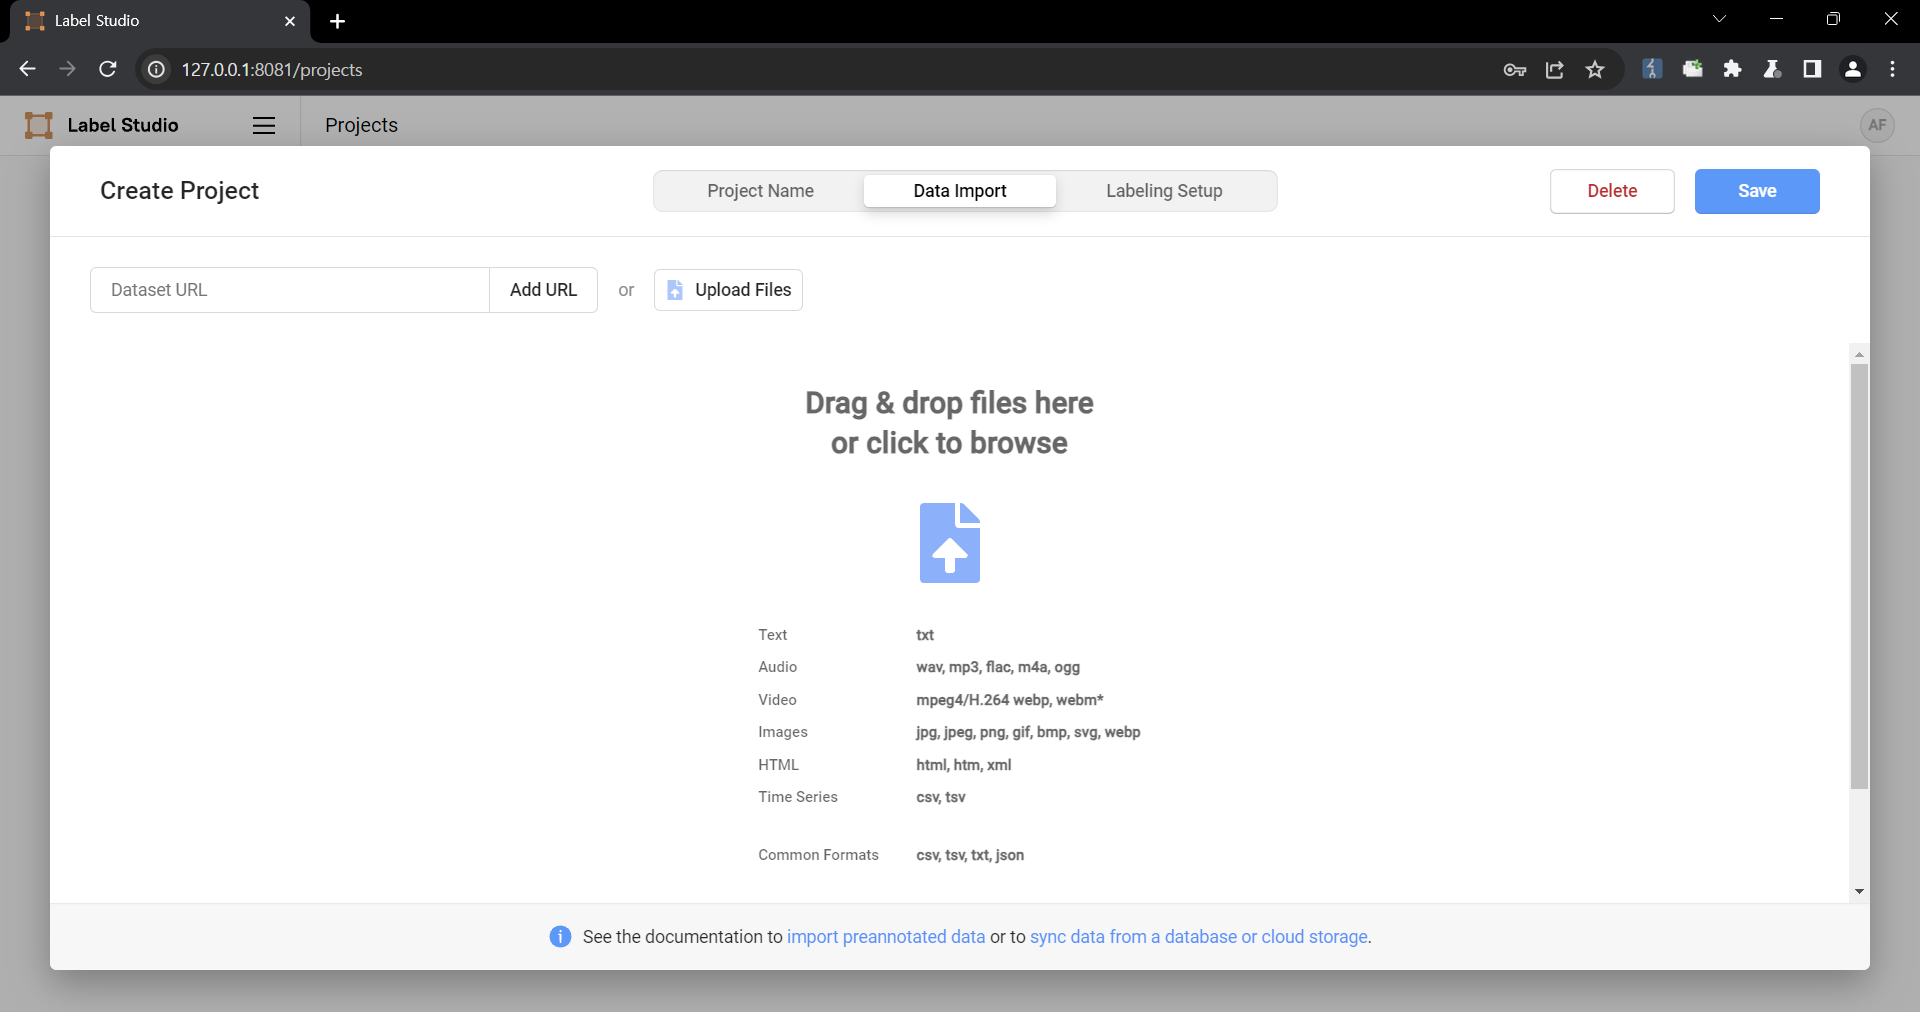
2. Upload a file containing the payload using the "Upload Files" function.
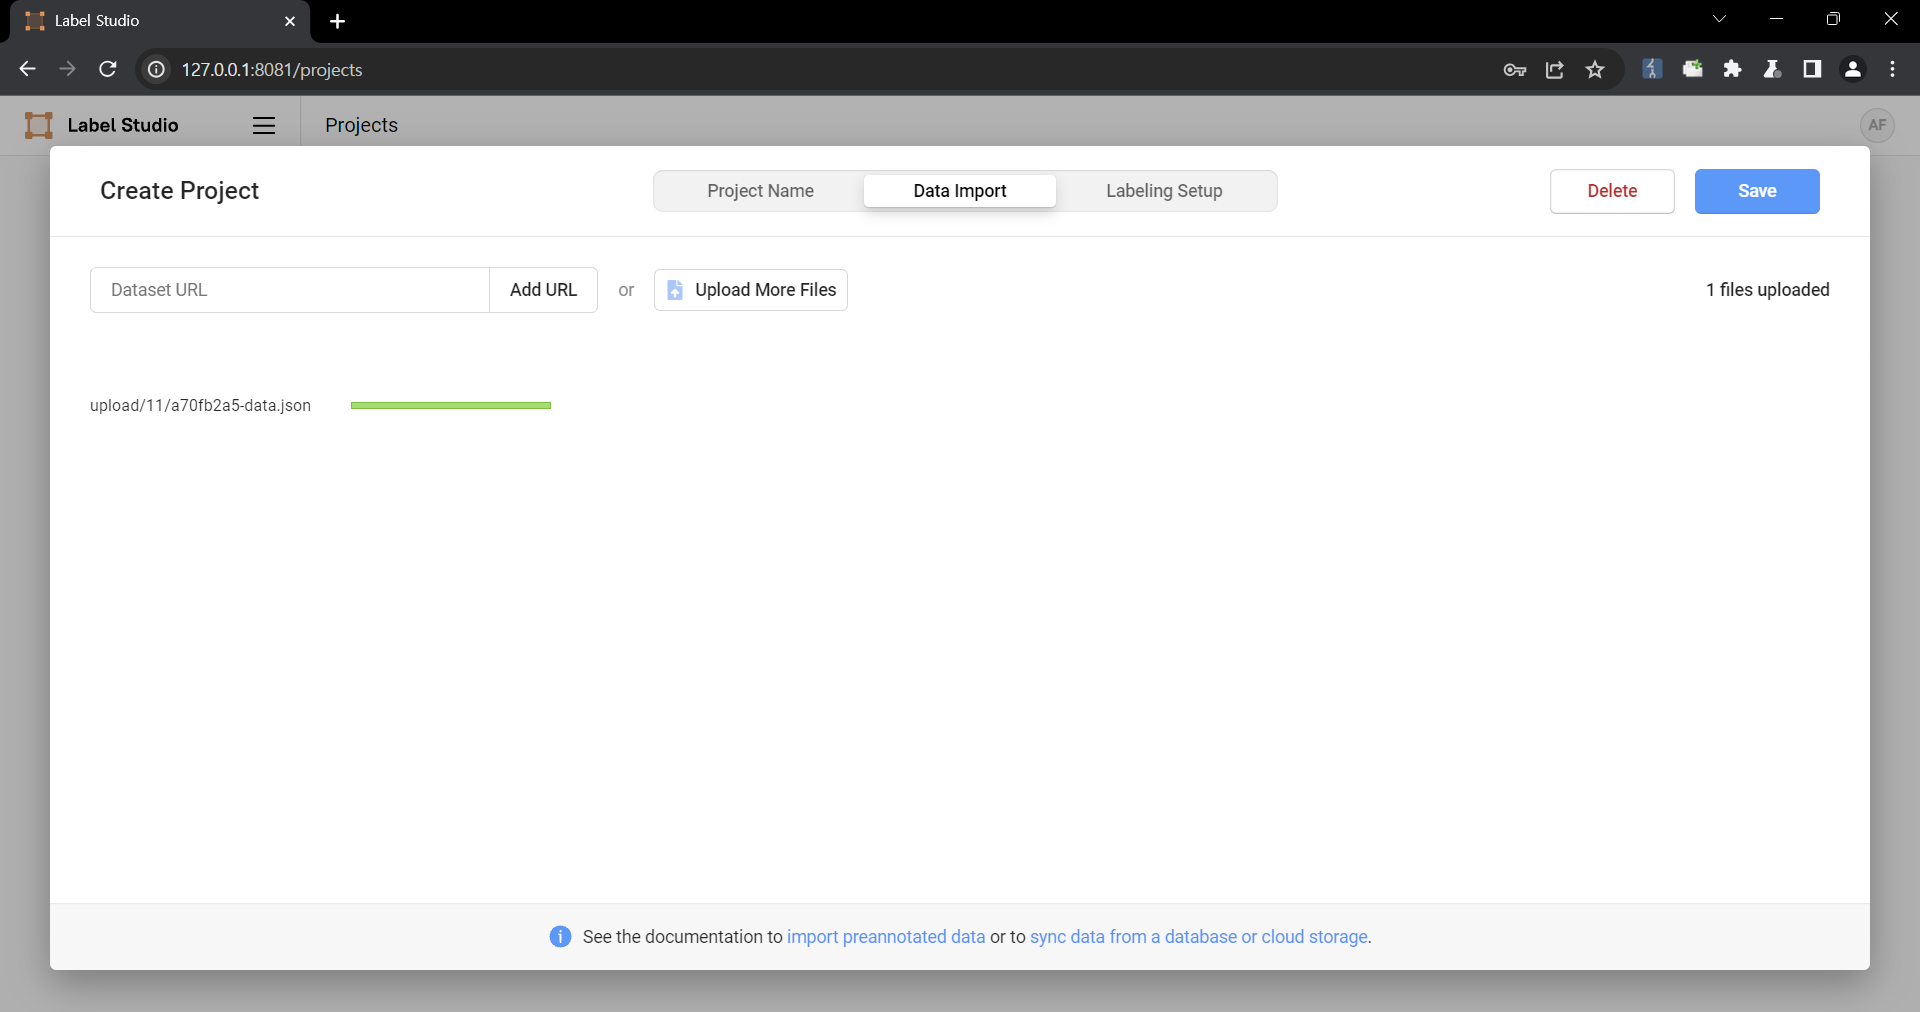
The following are the contents of the files used in the PoC
```
{
"data": {
"prompt": "labelstudio universe image",
"images": [
{
"value": "id123#0",
"style": "margin: 5px",
"html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>"
}
]
}
}
```
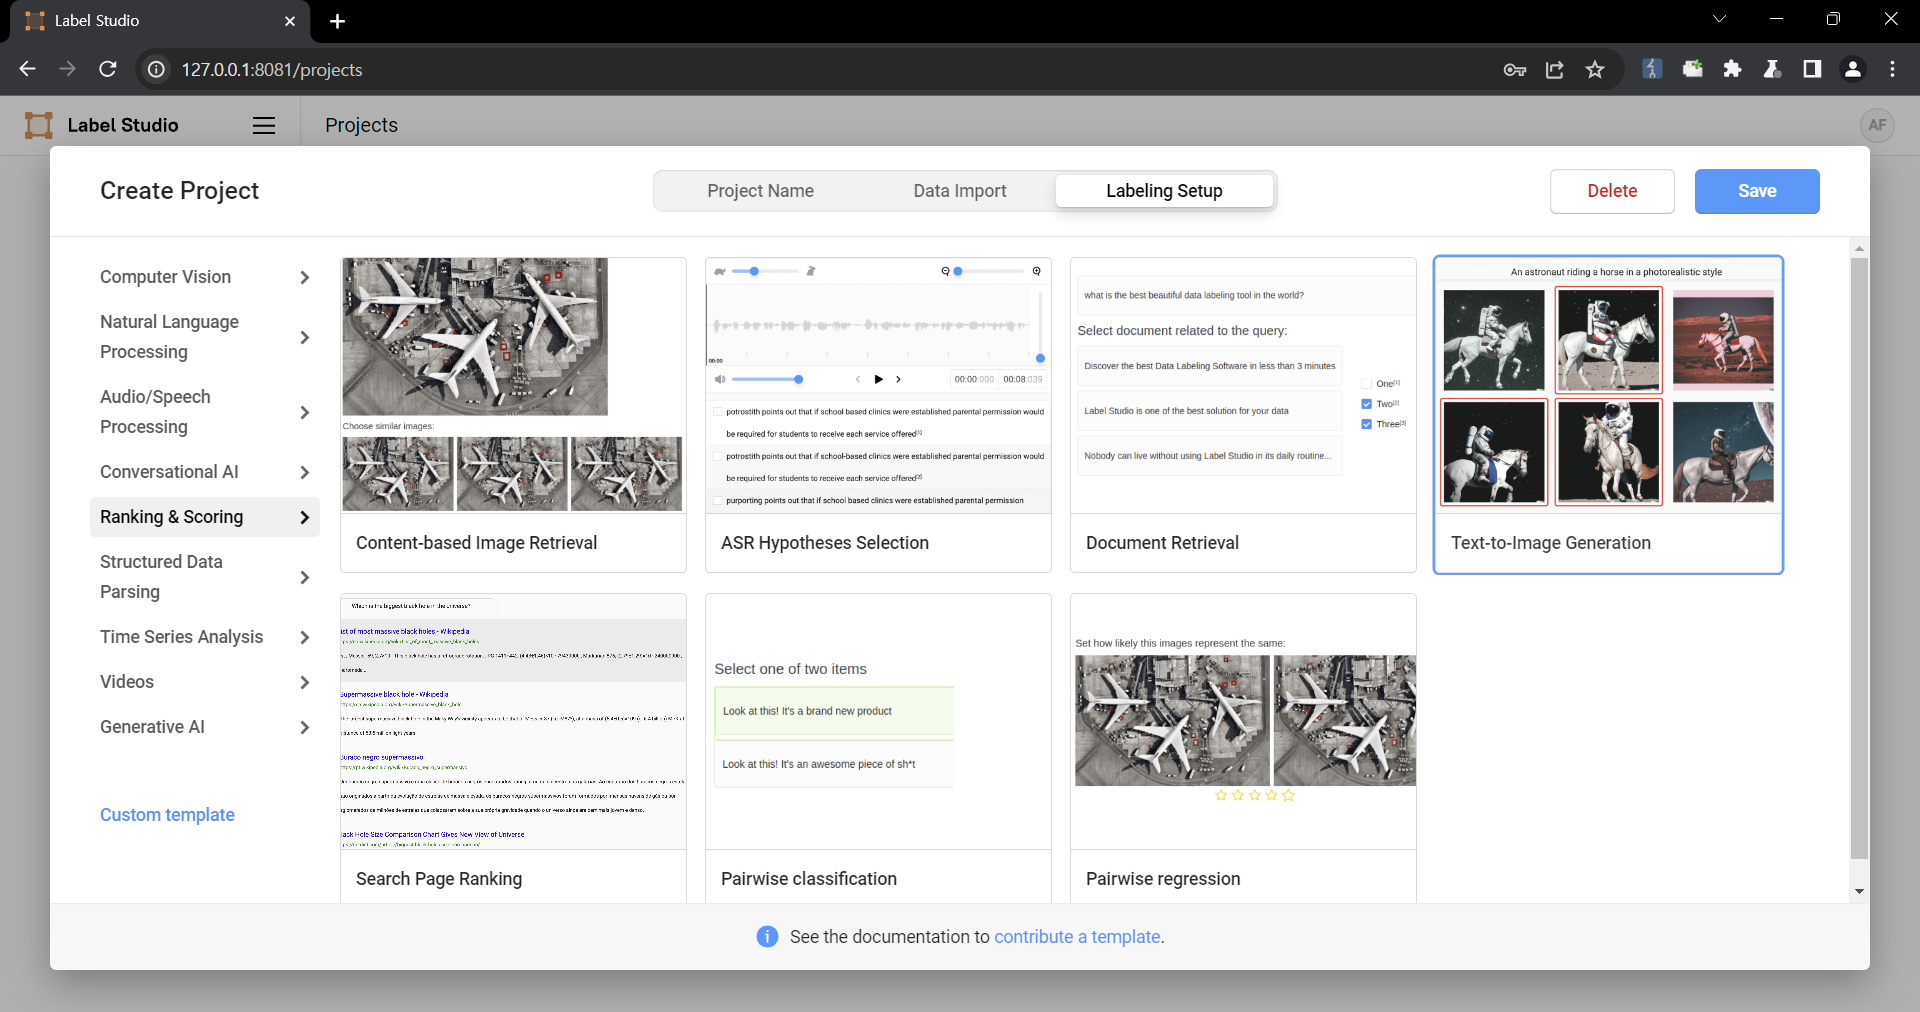
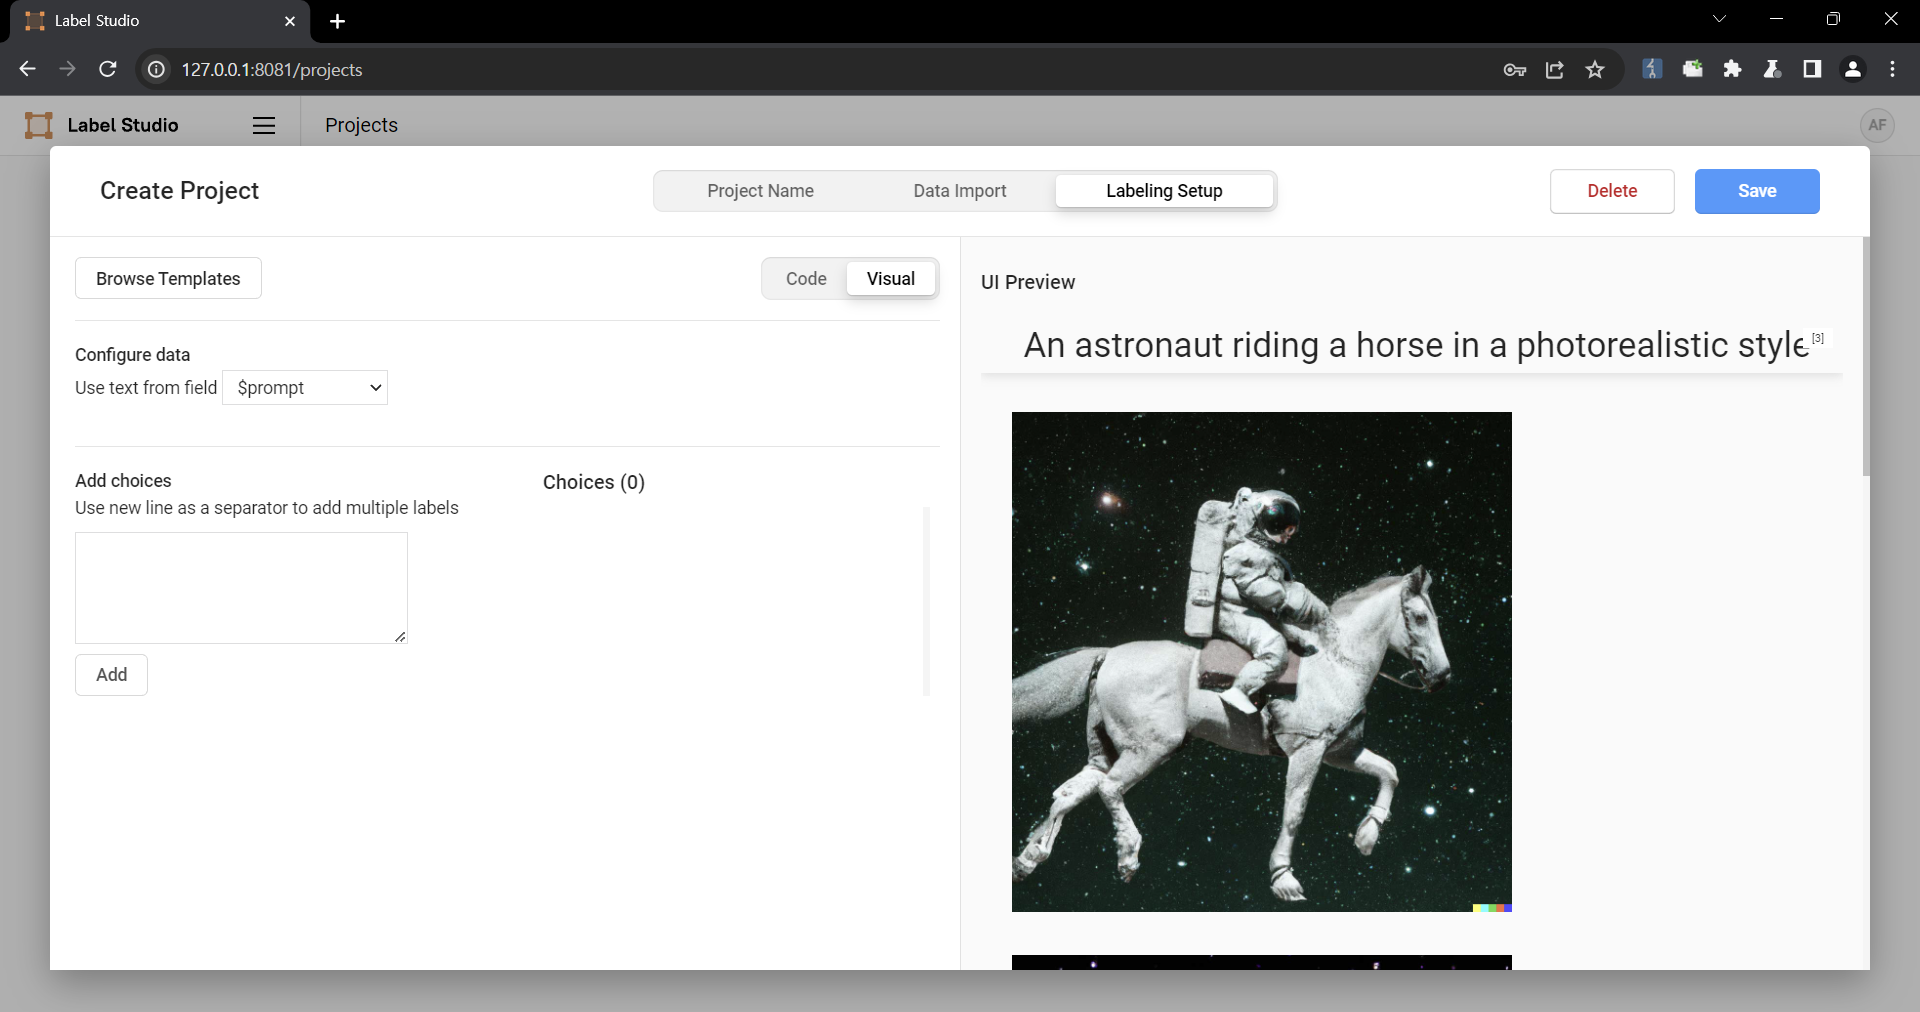
3. Select the text-to-image generation labeling template of Ranking and scoring
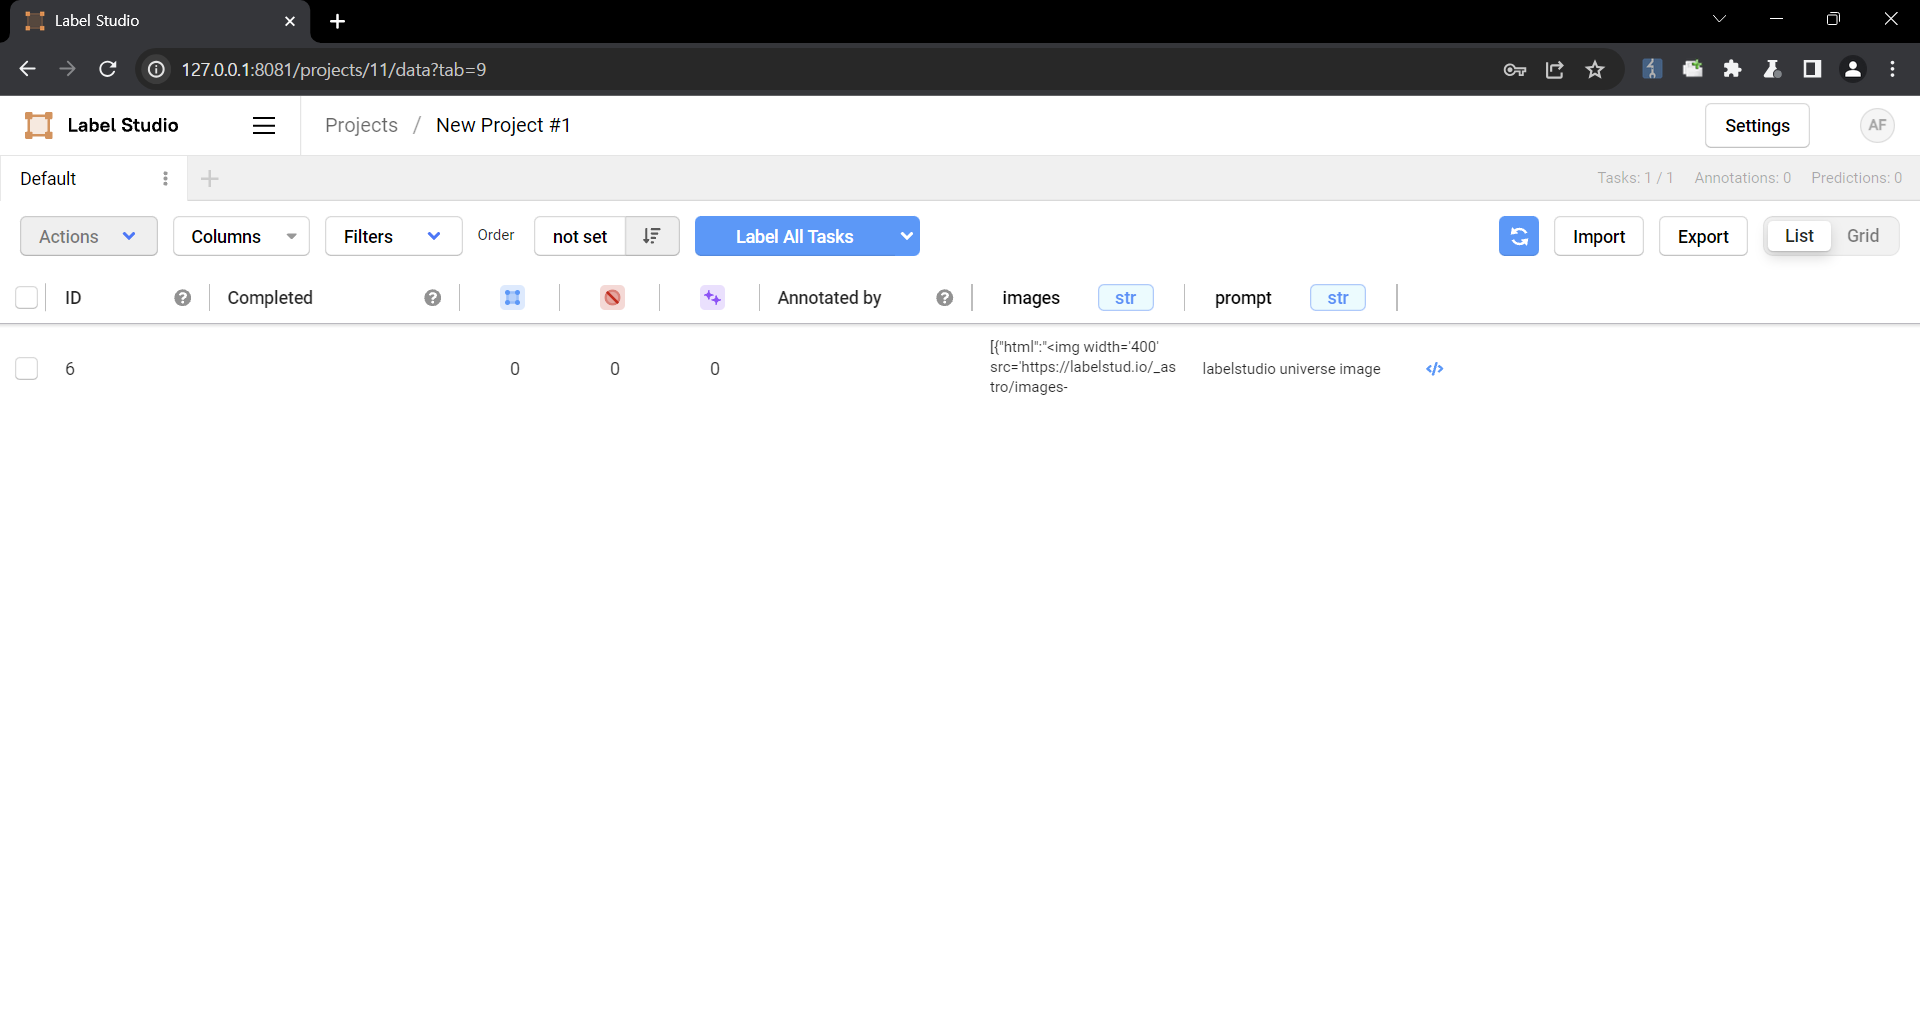
4. Select a task
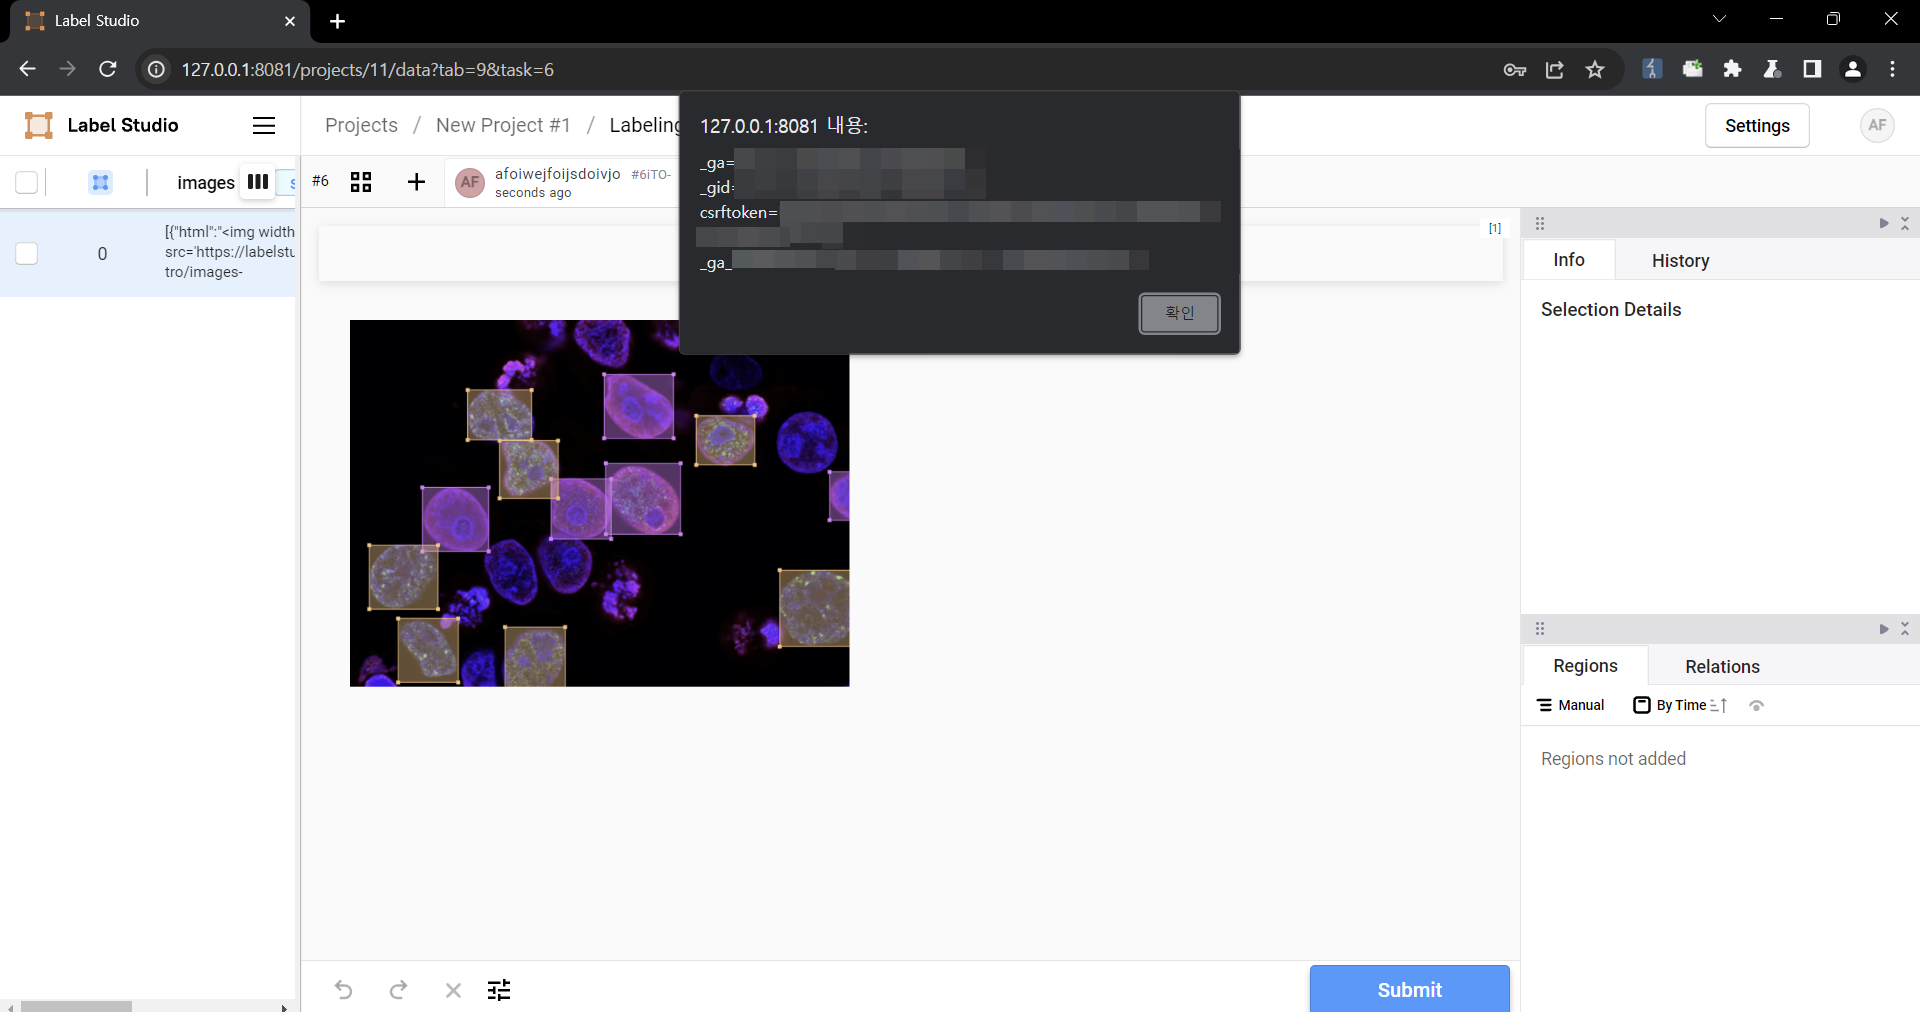
5. Check that the script is running
### Impact
Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Source: CVE Program / CVE List V5
CVSS Information
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N
Source: CVE Program / CVE List V5
Vulnerability Type
在Web页面生成时对输入的转义处理不恰当(跨站脚本)
Source: CVE Program / CVE List V5
Vulnerability Title
Label Studio 安全漏洞
Source: CNNVD (China National Vulnerability Database)
Vulnerability Description
Label Studio是Heartex开源的一个开源数据标注工具。允许您使用简单明了的 UI 标记音频、文本、图像、视频和时间序列等数据类型,并导出为各种模型格式。 Label Studio 1.11.0之前版本存在安全漏洞,该漏洞源于存在跨站脚本(XSS)漏洞。
Source: CNNVD (China National Vulnerability Database)
CVSS Information
N/A
Source: CNNVD (China National Vulnerability Database)
Vulnerability Type
N/A
Source: CNNVD (China National Vulnerability Database)
Affected Products
| Vendor | Product | Affected Versions | CPE | Subscribe |
|---|---|---|---|---|
| HumanSignal | label-studio | < 1.11.0 | - |
|
II. Public POCs for CVE-2024-26152
| # | POC Description | Source Link | Shenlong Link |
|---|
AI-Generated POC
Premium
No public POC found.
Login to generate AI POCIII. Intelligence Information for CVE-2024-26152
请登录查看更多情报信息。
Patches & Fixes for CVE-2024-26152 (2)
-
https://github.com/HumanSignal/label-studio/pull/5232 x_refsource_MISC
Vendor Advisories for CVE-2024-26152 (1)
Other References for CVE-2024-26152 (1)
-
https://github.com/HumanSignal/label-studio/releases/tag/1.11.0 x_refsource_MISC
IV. Related Vulnerabilities
Same product: label-studio
-
CVE-2026-85211
Label Studio through 1.23.0 Cross-Organization Storage URI R -
CVE-2026-85179
Label Studio through 1.23.0 SSRF via Unvalidated Webhook URL -
CVE-2026-76073
Label Studio through 1.23.0 Cross-Organization Annotation Ac -
CVE-2026-22033
Label Studio vulnerable to full account takeover by chaining -
CVE-2025-47783
label-studio vulnerable to Cross-Site Scripting (Reflected)
Same vendor: HumanSignal
-
CVE-2026-85211
Label Studio through 1.23.0 Cross-Organization Storage URI R -
CVE-2026-85179
Label Studio through 1.23.0 SSRF via Unvalidated Webhook URL -
CVE-2026-76073
Label Studio through 1.23.0 Cross-Organization Annotation Ac -
CVE-2026-72560
HumanSignal Label Studio - Server-Side Request Forgery -
CVE-2026-22033
Label Studio vulnerable to full account takeover by chaining
Same weakness: CWE-79
-
CVE-2026-105291
feelec-yishu feelcrm-os Department Search Endpoint GroupCont -
CVE-2026-59788
Stored XSS vulnerability in OAuth configuration form -
CVE-2026-105289
feelec-yishu feelcrm-os Create Customer Endpoint CrmDefineFo -
CVE-2026-105288
feelec-yishu feelcrm-os Crm Endpoint functions.php index cro -
CVE-2026-102393
WordPress Starter Templates plugin <= 4.7.7 - Cross Site Scr
V. Comments for CVE-2024-26152
No comments yet