WordPress Page Builder KingComposer <=2.9.6 - Open Redirect
<div align="center">
<img src="https://blogs.cappriciosec.com/uploaders/CVE-2022-0165-tool.png" alt="logo">
</div>
## Badges
[](https://choosealicense.com/licenses/mit/)


<a href="https://github.com/Cappricio-Securities/CVE-2022-0165/releases/"><img src="https://img.shields.io/github/release/Cappricio-Securities/CVE-2022-0165"></a>
[](https://twitter.com/cappricio_sec)
<p align="center">
<p align="center">
## License
[MIT](https://choosealicense.com/licenses/mit/)
## Installation
1. Install Python3 and pip [Instructions Here](https://www.python.org/downloads/) (If you can't figure this out, you shouldn't really be using this)
- Install via pip
- ```bash
pip install CVE-2022-0165
```
- Run bellow command to check
- `CVE-2022-0165 -h`
## Configurations
2. We integrated with the Telegram API to receive instant notifications for vulnerability detection.
- Telegram Notification
- ```bash
CVE-2022-0165 --chatid <YourTelegramChatID>
```
- Open your telegram and search for [`@CappricioSecuritiesTools_bot`](https://web.telegram.org/k/#@CappricioSecuritiesTools_bot) and click start
## Usages
3. This tool has multiple use cases.
- To Check Single URL
- ```bash
CVE-2022-0165 -u http://example.com
```
- To Check List of URL
- ```bash
CVE-2022-0165 -i urls.txt
```
- Save output into TXT file
- ```bash
CVE-2022-0165 -i urls.txt -o out.txt
```
- Want to Learn about [`CVE-2022-0165`](https://blogs.cappriciosec.com/cve/169/%20The%20KingComposer%20WordPress%20Plugin%20Open%20Redirect%20Vulnerability%20(CVE-2022-0165))? Then Type Below command
- ```bash
CVE-2022-0165 -b
```
<p align="center">
<b>🚨 Disclaimer</b>
</p>
<p align="center">
<b>This tool is created for security bug identification and assistance; Cappricio Securities is not liable for any illegal use.
Use responsibly within legal and ethical boundaries. 🔐🛡️</b></p>
## Working PoC Video
[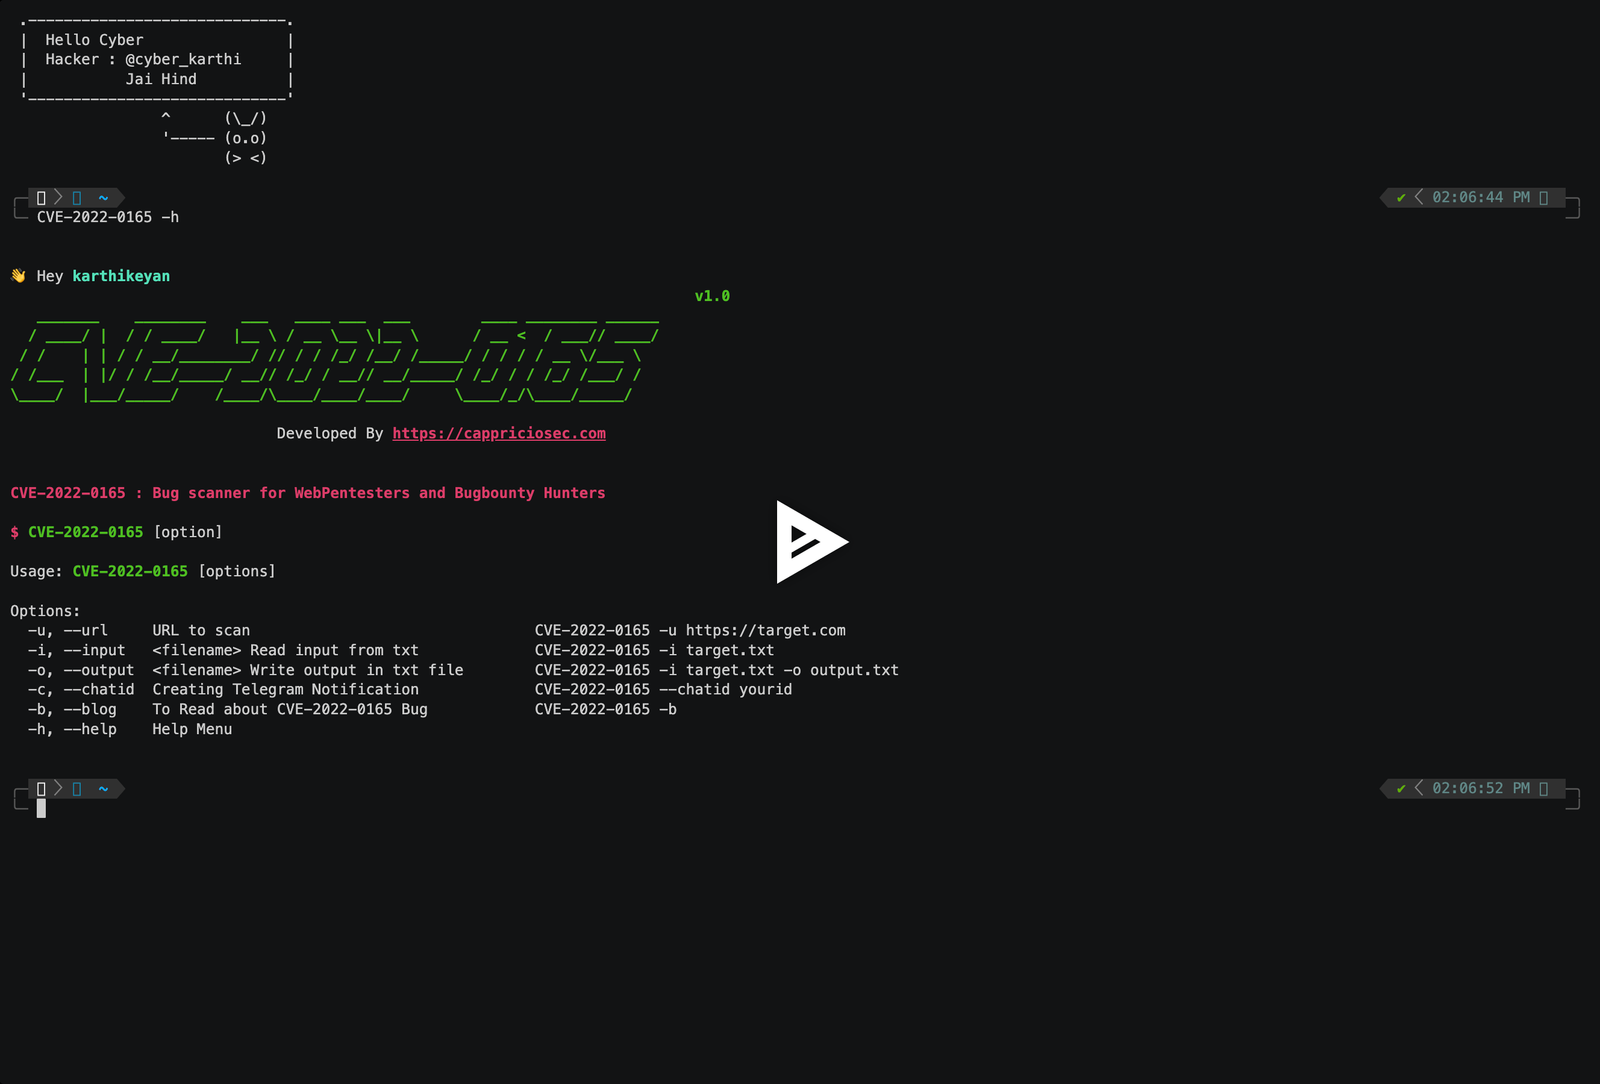](https://asciinema.org/a/hRPt1UYVR4jINKx2JPdnrqVV8)
## Help menu
#### Get all items
```bash
👋 Hey Hacker
v1.0
_______ ________ ___ ____ ___ ___ ____ ________ ______
/ ____/ | / / ____/ |__ \ / __ \__ \|__ \ / __ < / ___// ____/
/ / | | / / __/________/ // / / /_/ /__/ /_____/ / / / / __ \/___ \
/ /___ | |/ / /__/_____/ __// /_/ / __// __/_____/ /_/ / / /_/ /___/ /
\____/ |___/_____/ /____/\____/____/____/ \____/_/\____/_____/
Developed By https://cappriciosec.com
CVE-2022-0165 : Bug scanner for WebPentesters and Bugbounty Hunters
$ CVE-2022-0165 [option]
Usage: CVE-2022-0165 [options]
```
| Argument | Type | Description | Examples |
| :-------- | :------- | :------------------------- | :------------------------- |
| `-u` | `--url` | URL to scan | CVE-2022-0165 -u https://target.com |
| `-i` | `--input` | filename Read input from txt | CVE-2022-0165 -i target.txt |
| `-o` | `--output` | filename Write output in txt file | CVE-2022-0165 -i target.txt -o output.txt |
| `-c` | `--chatid` | Creating Telegram Notification | CVE-2022-0165 --chatid yourid |
| `-b` | `--blog` | To Read about CVE-2022-0165 Bug | CVE-2022-0165 -b |
| `-h` | `--help` | Help Menu | CVE-2022-0165 -h |
## 🔗 Links
[](https://cappriciosec.com/)
[](https://www.linkedin.com/in/karthikeyan--v/)
[](https://twitter.com/karthithehacker)
## Author
- [@karthithehacker](https://github.com/karthi-the-hacker/)
## Feedback
If you have any feedback, please reach out to us at contact@karthithehacker.com
Log in to view the POC file snapshot cached by Shenlong Bot
Log in to view