# CVE-2023-4698
# Local File Inclusion (LFI) in usememos/memos < 0.13.2
## Description
Today, I want to shine a spotlight on a significant discovery — a critical security vulnerability that has been identified in usememos/memos. This vulnerability, which falls under the category of Local File Inclusion (LFI), poses a grave threat to systems running versions of usememos/memos earlier than 0.13.2. This issue has been assigned the CVE identifier CVE-2023–4698. In this blog post, we’ll dissect this vulnerability, understand its implications, and emphasize the urgency of addressing it.
## Understanding the LFI Vulnerability
At the heart of this vulnerability is a Local File Inclusion (LFI) flaw. This type of vulnerability allows attackers to read arbitrary files on a server by exploiting weaknesses in the code. Specifically, this vulnerability arises from a flaw that enables attackers to manipulate the “InternalPath” parameter in a request, ultimately leading to the inclusion of files from the server’s file system.
## Proof of Concept
[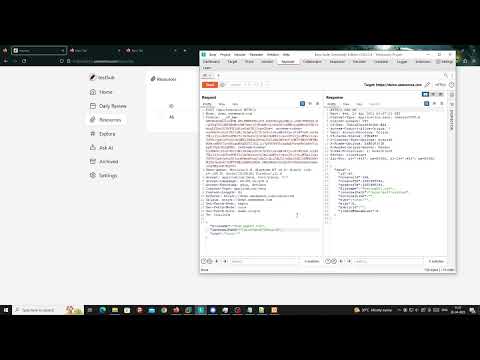](https://youtu.be/BvfttobD8hU)
## Impact of the Vulnerability
The implications of successfully exploiting the Local File Inclusion (LFI) vulnerability are far-reaching and deeply concerning. For systems running affected versions of usememos/memos (< 0.13.2), the consequences can include:
Data Theft: Attackers can access sensitive files, such as configuration files and databases, potentially leading to data theft and privacy breaches.
Server Compromise: In certain scenarios, LFI can escalate into Remote Code Execution (RCE), granting attackers the ability to execute arbitrary code on the target system, potentially resulting in complete server compromise.
Secondary Attacks: LFI can serve as a stepping stone for launching additional attacks, including Directory Traversal, Server-Side Request Forgery (SSRF), or Denial of Service (DoS). These attacks can further compromise the system or disrupt its normal operation.
## Identifying the Vulnerable Code
This vulnerability stems from the code itself, primarily within the "resource.go" file, spanning lines 1 to 69. The core issue lies in the inadequate validation and sanitization of user input for the "InternalPath" field. This oversight enables attackers to supply a malicious value for "InternalPath" when creating or updating a Resource. This malicious input is then blindly utilized to access sensitive files within the server's file system.
For instance, an attacker might set the "InternalPath" field to "/etc/passwd" or "/proc/self/environ," attempting to retrieve sensitive files from the server. As a result, the server inadvertently discloses the contents of these internal files, potentially exposing highly sensitive information.
## References
For more details on this vulnerability, please refer to the following resources:
- [huntr.dev Report](https://huntr.dev/bounties/e1107d79-1d63-4238-90b7-5cc150512654/)
- [Medium Blog - Local File Inclusion (LFI) in usememos/memos < 0.13.2](https://medium.com/@mnqazi/cve-2023-4698-local-file-inclusion-lfi-in-usememos-memos-0-13-2-d5008ddb014b)
You can also follow me for updates on my research and other security-related topics:
- Instagram: [@mnqazi](https://www.instagram.com/mnqazi)
- Twitter: [@mnqazi](https://twitter.com/mnqazi)
- Facebook: [@mnqazi](https://www.facebook.com/mnqazi)
- LinkedIn: [M Nadeem Qazi](https://www.linkedin.com/in/m-nadeem-qazi)
Let's prioritize security and protect our systems from potential threats. Stay vigilant! 💻🔒
Log in to view the POC file snapshot cached by Shenlong Bot
Log in to view